 The 2026 Drupal Business Survey is open. Your response will help shape the future of the Drupal business ecosystem.
How to create sub group in D8 version

 The 2026 Drupal Business Survey is open. Your response will help shape the future of the Drupal business ecosystem.
How to create sub group in D8 version
| Comment | File | Size | Author |
|---|---|---|---|
| #271 | port-subgroups-2736233-271.patch | 117.34 KB | andrewsizz |
| #270 | port-subgroups-2736233-270.patch | 117.33 KB | andrewsizz |
| #261 | interdiff-254-261.txt | 12.4 KB | lobsterr |
| #261 | port-subgroups-2736233-261.patch | 141.16 KB | lobsterr |
| #255 | interdiff_253-254.txt | 3 KB | adrianodias |




Comments
Comment #2
kristiaanvandeneyndeAlthough, this could be easily enabled by writing a small plugin, the Group 7 version of this did a lot more. I.e.: membership inheritance and synchronization. This is on the to-do-list, but only as an addition after a 1.0 release.
Comment #3
jludwig commentedAttached is a patch to get things rolling here. This will allow you to add existing/new subgroups and view an overview off all the subgroups associated with a group.
Not this much code was needed to actually allow subgrouping functionality (the minimum would be basically just the content enabler plugin), but this was created by basically copying the gnode module and changing it to deal with groups instead of nodes, so implements all of the same functionality that gnode does except... (get this)...
...Access control!
So this is put as needs work, because it needs:
- Stronger access control
- Features from the D7 version (membership inheritance, synchronization, etc)
- It should probably be treated more uniquely. Not everything in the gnode module makes sense in the module and vice-versa.
This is still, however, very usable if all you need to do is add groups to groups.
Cheers!
-Justin
Comment #4
matslats commentedThis looks more thorough than my contribution at https://www.drupal.org/node/2699287
I'm keen to get this committed because I have a lot to build on top of it.
Comment #5
zerolab commentedComment #6
jludwig commentedHey matslats,
I didn't see that base module that you had committed in that other issue. Sorry! that would have been a good place to start from and it looks almost exactly like the plugin I had written before fleshing it out.
kristiaanvandeneynde, make sure to give matslats some credit if this goes in because his contribution is pretty much exactly what we talked about at DrupalCon.
Comment #7
kristiaanvandeneyndeRight closing the other issue then in favor of this one.
Just to emphasize the instructions I wrote there:
Comment #8
kristiaanvandeneyndeAdding matslats to the fixed credit receivers.
Comment #9
matslats commentedThe conventional way to create new entities here and in gnode in a group is to provide a new entity form to create the entity, then redirect to another form which creates the GroupContent.
This is a weird user experience though. What if we made a CreateEntityForm for every contentEntity?
group/{group}/node/add/storywhich inherits everything but in the submit method, it just creates the groupContent
Comment #10
alan.upstone commented#9 Gets my vote. My users don't care about the relation. I care a lot as the site builder but they just want to create content. It's me that has divided them into groups.
In the current two-step process, they say "Didn't I just do that?"
Comment #11
matslats commentedWell here's how I'm doing it
Comment #12
kristiaanvandeneyndeThe need to hide the relationship form is a strong sentiment I want to cater to. The first iteration of that crashed and burned as I realized we would potentially have a security issue, incomplete data and a performance hit on our hands.
Maybe we should open a ticket to discuss the options regarding the workflow in the Group Node module and then copy the solution we found there into Subgroup?
Comment #13
matslats commented>security issue, incomplete data and a performance hit
Does this apply to my solution in #11?
How does organic groups module do it?
Comment #14
kristiaanvandeneyndeWhen I tried a version where you could have the form auto-submit itself, I came to realize that links such as /group/X/join would also auto-submit the form, meaning we are open to click-jacking attacks.
So ideally, there needs to be a setting on the plugin that allows you to choose whether you want to use the wizard (2-step) or just the node creation form (1-step). That way, we do not risk having auto-submitting links that could potentially be click-jacked.
Comment #15
matslats commentedI see the problem but you didn't comment on either of my two ideas.
1) Dynamically create a new entityForm for every GroupContent plugin installed with a new path prefix (which informs the route context) then use the submit handler of that extended entityForm to create the GroupContent entity.
2) Create new routes for every GroupContent plugin installed and use the entity create hook to get the group from context, and create the GroupContent with the hook_entity_insert
Both of these approaches involve making a new route with the group in, which means new content can go into a maximum of one group.
Comment #16
matslats commentedStill hoping for answers for #15. But this is a question about the new subgroup module.
There is a global group permission (appears in every group) called Access subgroup overview.
Seems to me it should only appear in groups with subgroups, no?
In which case the permission should be declared in
Drupal\ggroup\Plugin\GroupContentEnabler\SubGroup::getPermissions
and referenced in
Drupal\ggroup\Plugin\GroupContentEnabler\SubGroup::getGroupOperations
Comment #17
kristiaanvandeneyndeI'll have a thorough look at #15 shortly. Probably tomorrow.
Comment #18
kristiaanvandeneyndeRe #15:
1) I would not like to add or generate individual forms per plugin. I'd prefer to have a solid base for every scenario that other modules could then extend or alter. E.g.: CreateContentInGroupForm and GroupContentCreateWizardForm.
2) We just abandoned the path of generating routes for every single group content type (plugin) because it was too annoying to maintain. I'd prefer to see paths such as:
group/1/content/relate/{entity_type_id}to add existing entitiesgroup/1/content/add/{entity_type_id}to add new entities to the groupWhere the latter path would either use the simple for or the wizard as outlined in my reply to your first suggestion.
The key here is simplicity and reusability. We want solutions that offer good UX in the front end, without sacrificing developer sanity in the process. Having code that's easy to extend or re-use is the key to make the module loved by developers as well.
Re #16, that permission could perhaps be used for a view at group/X/groups. Much like the group node and members view.
Comment #19
matslats commentedI can develop this, but I need clearer instructions.
I don't see in your last comment which way you want to avoid a second stage form.
Comment #20
kristiaanvandeneyndeI would use a plugin config with radio buttons:
When people want to create content in this group they:
Warning: If you configured fields on the relationship, these will not be filled out!
Then based on that setting, we could fire up the wizard or the single creation form. Relating content to groups can keep using the form we already have. I.e.: With the entity reference field and the relation's configured fields.
Plugins could then choose which option they want to default to and call it a day. They could even choose to lock the setting and not show the radio buttons if it would break when another method is selected; e.g.: group_membership
Comment #21
matslats commentedOK that's clear
How will 'my_entity's creation form be built for the second option?
Will the original creation form be altered by the ContentEnabler plugin?
Will it add a submit handler which creates the groupcontent?
Comment #22
kristiaanvandeneyndePlease see #2796197-24: Group or Group Node generates some massive queries, we will have to remove
hook_group_user_roles_alter(). If you want to move this issue ahead, look at the approach in Group 7. It involves saving memberships and linking those back to the parent that allowed them to exist.This one just got more complicated sadly, but it's to allow us to have consistent cache contexts and performant grants, so it has to be done.
Comment #23
matslats commentedI don't see the connection, and I'm not going to get involved in that other issue.
While I'm waiting however, and building my own distro on groups, and my own contentEnabler plugins, any directions you can give about how this issue is going to work out would be appreciated.
Comment #24
kristiaanvandeneyndeThe connection is that the hook we could have used to make Subgroup a really simple and streamlined module, will have to be removed.
Comment #25
CalebD commentedI'm interested in contributing some development of the subgroups feature. We need it for a project we're working on. Has anyone made any additional progress toward kristiaanvandeneynde's outlined approach in comment #7 starting with jludwig's module in comment #3? I'd like to start from whatever has the most progress toward the functionality.
Comment #26
jludwig commentedThe code I added in #3 did the following out of #7:
It does some more, but does not approach these:
Comment #27
kristiaanvandeneyndeGreat to see other people working on this. Thanks guys!
Comment #28
CalebD commentedI just wanted to say that I do plan on starting in on this effort either tomorrow or Monday. We had to focus on getting our Group setup configured first.
Comment #29
CalebD commentedComment #30
dmiric commentedGgroup module can not be enabled if there are no groups on the site. Basically form installation profile.
It returns:
Comment #31
jludwig commentedAye. gnode has the same issue if no content types have been defined.
Comment #32
kristiaanvandeneyndeHas anyone submitted a bug report for that?
Comment #33
CalebD commentedKristiaan, wondering if you have any additional thoughts on how this should work? I wrote some ideas below. Interested in what you agree or disagree with.
Here is a thought experiment concerning groups, subgroups, and user membership. If Group B is added as a subgroup of Group A, then all members of Group B can be said to be indirect members of Group A (agreed?). Should
$group_a->getMembers();return a flattened list of all members of Group A and Group B (and descendant groups, recursively)? What about the other way around? I am thinking$group_b->getMembers();shouldn't return Group A members because membership is recursive descent? Roles could be recursively mapped into the roles of Group A.I looked at the Drupal 7 version of ggroup and it seems to have an inheritance concept whereby
group_membershipentities are created based on inheritance configuration. I'd like to avoid anything like that and make the behaviors of subgroups as seamless and intuitive as possible. There seems to be a lot of fuzziness in how certain things could be handled.Basically, I can come up with some behaviors based on how we'd like it to work for our use case, but if we're going to contribute back I'd like to build something that the community could use.
Comment #34
jludwig commented@CalebD IMO, that's a tough one. I, for one, would not want the children to inherit the memberships because I would want to know exactly who is in that specific child. No more, no less.
A good example is the university setting. You wouldn't want every single person in a department to be a part of the classrooms associated with that department, right? Otherwise, that department member might be in dozens of groups, receive emails for dozens of groups, etc, and you wouldn't know if they were really a part of that group or a part of the staff overseeing the classroom.
Permissions, on the other hand, make sense. The members of the department, with the right permissions, should be able to see basically anything in any classroom that is associated with the department.
If we cannot comet to an agreement, I would at least argue that this should be configurable. Both functionalities make sense in certain circumstances.
Comment #35
CalebD commented@jludwig, in that scenario if the department is a group and the classes are each a group, and the class groups are part of the department group, then
$department->getMembers();would return a list of everyone directly in the department group as well as all the class members, while$some_class->getMembers();would return only the members of the class because what I was proposing is that membership is only inherited by descent. Or am I misunderstanding your example? Either way, I do agree that direct inheritance may not be desired, or there needs to be a way to disambiguate between direct and indirect members. Maybe it is a configuration option on the plugin?My use case is using the
gnodeto control access to content. We have a lot of different groups of users. To grant access to some content, instead of adding a node to all those groups, we'd prefer to add the node to a "grouping" group, one that has all the user groups added as subgroups. Then in the future if we have another group of users who need access to that content, we just add their group to the grouping group as a subgroup and those users would be given the same node access permissions.Parent "grouping" group ← node added to this group, permissions grant members view access Child subgroup ← users added to this groupGiven that you created the initial D8 version of
ggroup, what was the use case?Comment #36
CalebD commentedOne approach I am thinking about is having
ggroupmaintain the hierarchy data of the subgroups.GroupMembershipLoaderwould be modified to fire events when loading memberships giving other modules a chance to react.ggroupwould react by looking at the given group, finding the proper content plugin, checking if an "inherit membership" option is enabled, and if so pulling group membership for all descendant groups in the hierarchy to add to the event data.Group hierarchy would be stored by having
ggroupcreate a text field on the group content type that would store hierarchy data using the "path enumeration" technique (similar to how Drupal stores comment thread structures). Querying against that field should allow for efficient joins to grab the membership of all descendant groups given a starting group.Interested in feedback. Thanks!
Comment #37
CalebD commentedI realized my use case is more complex than I originally realized. Because a group can have any number of child groups and a group can have any number of parent groups, the result is a graph structure. Unfortunately relational databases don't excel at dealing with graphs. I'm currently researching approach ideas.
As an aside, I recognize my use case is probably much more complex than others. We're wanting to build a flexible access control system and groups within groups is a core component of that flexibility. I don't want to derail anyone else's vision of how this could be implemented, so I'm still interested in input from others.
Comment #38
matslats commentedI'd appreciate if we could have some code committed here, just to be going on with. I've built a lot on jludwig's patch and I've things to add.
- a block showing subgroups of the current group
- a devel_generate base plugin
Comment #39
kristiaanvandeneyndeThis would be a good way to deal with things. We should avoid having code in the Group class that knows there may be subgroups. Firing events from within the
GroupMembershipLoaderwould be great.That said, I do not think we should have an unconfigurable inheritance system. We now have the benefit of configurable plugins, so let's use those to their best abilities. The UI we have in place in D7 could use some UX love, but it's a good start.
Like in D7, synchronizing memberships so that we actually have them in the database is a good solution too. So far, relations have always been top-down but do we also want to cater to bottom-up?
A teacher in a faculty should get privileges in all class rooms there (top-down). But do we also want to let students from those class rooms see a faculty-only message (bottom-up)? In that case, we need to be careful that inherited memberships do not trigger an endless loop.
Comment #40
matslats commentedSound to me like the subgroup Enabler plugin needs to have an option to inherit membership from the parent or to create memberships in the parent or do nothing.
I would be happy to add that feature if you give me the go-ahead.
Comment #41
kristiaanvandeneyndePlease look at the way the D7 ggroup module does it to get an idea of what that inheritance option may look like. But yeah, feel free to work on something already :)
Comment #42
matslats commentedI've installed d7 and looked at it. I see how the roles inherit.
What I was offering to do was create the mechanism for passing members up and down the hierarchy when groups are created, which is what CalebD was talking about.
Shouldn't that be done first, then it can be extended to handle roles other than 'member'?
Comment #43
CalebD commentedmatslats, I'm not sure if you've started any work on what you mentioned, but I've made progress on my own approach for subgroups. The code needs a bit more work to support basic functionality. I ended up figuring out my own approach based on our needs rather than look at D7 ggroup. I wanted a solution that could quickly determine group membership via a hierarchy without having to synchronize membership content entities into each group. It also needs to prevent circular references in the hierarchy (Group A has Group B has a subgroup, Group B has Group A as a subgroup, and any other extended derivative).
Once I have the rest of the basics working I'll post a patch for others to look at. Either later today or tomorrow.
Comment #44
sriharsha.uppuluri commented@CalebD - Waiting for the patch :) . In our project we need subgroup module.
Comment #45
CalebD commentedHere is my work in progress on subgroups. THIS PATCH IS A PROTOTYPE AND IS NOT READY FOR PRODUCTION USE! This patch is built on the work started by jludwig. What follows is an explanation of what it currently does and how.
First I'll explain the functionality I'm solving for in my approach. My need is around group hierarchies and memberships. Members of subgroups should be considered as indirect members of the supergroup (parent group). For example, given group A and group B, such that group B is a subgroup of group A, then all direct members of group B are indirect members of group A. Now extend that relationship and behavior out to arbitrarily complex group hierarchieries, like this one. Upon doing so we realize that such a hierarchy can be described as a graph.
Other things to consider:
With more thought, we realize that a group hierarchy is a specific type of graph, called a directed acyclic graph (a DAG). To store the group hierarchy effectively, we need to store and traverse a DAG quickly. Unfortunately hierarchieries are not something that relational databases excel at storing and traversing. There are a variety of approaches for storing trees, but a DAG is more complex. Research brought me to this great article, which proposes a way to store the graph structure in a single table and query relationships quickly at the expense of storage. This is because the approach uses the graph structure to create a relationship between every connected entry in the graph, e.g. if group A has subgroup B, which has subgroup C, then a row will be added connecting A to C. Simple queries can be used to answer questions like "What are all the subgroups of this group?" or "What are all the supergroups of this group?". This is good for performance.
In studying the code for the
groupmodule, my assesment was that the best way to implement my needed functionality would be to modify the\Drupal\group\GroupMembershipLoaderso that memberships could be influenced by other providers. Drupal core uses events in a few areas for this purpose, for example with building and altering routes. The need to "build and alter" group memberships is similar. This approach allows modifying group membership transparently so that other modules, likegnode, do not need any modification.So, in this patch the
ggroupmodule defines a table,group_graph, that is used to store the group hierarchy graph. This information is in addition to thegroup_contentsubgroup entities that are created. When a subgroup entity is inserted, thegroup_graphtable is updated with the group hierarchy. There is a service class,\Drupal\ggroup\Graph\SqlGroupGraphStoragewhich handles all the database work, and a more general service class,\Drupal\ggroup\GroupHierarchyManagerwhich is a wrapper around the storage class and is what other classes should use to interact with the group hierarchy. A constraint is added togroup_contentsubgroup entity type so that circular group hierarchieries cannot be created.The patch also modifies
GroupMembershipLoaderto dispatch events when loading memberships, as mentioned above. Theggroupmodule implements an event subscriber which uses theGroupHierarchyManagerservice to pull group hierarchy. The event subscriber creates transientgroup_contentmembership entities which are added to the membership collection provided by the events. The transientgroup_contentmembership entities represent indirect memberships in a group and are not saved (though they should probably be cached but aren't currently).With the patch, this is what you can do:
group_graphtable is updated with the proper hierarchical representation.gnode.GroupHierarchyManager, can be used to easily query for subgroups and supergroups.Here is what is missing from this patch:
Some other thoughts:
GroupMembershipLoaderdispatches three different events. I wonder if this could be simplified?GroupMembershipLoaderByUserGroupEvent, which is really long. Any of the names of classes, methods, could and should be changed.I invite others in this thread to take a look and provide feedback. Thanks!
Comment #46
CalebD commentedHere is a very small update to my previous patch to fix a bug I noticed with the event subscribers. I haven't had time for further development unfortunately.
Comment #47
kaizerking commentedis sub groups module working? has any one tested #46?
Comment #48
matslats commentedI'm working with a much earlier version and it is functional.
The module mostly declares group as a groupcontent type.
There's a lot of stuff about inheriting permissions not done yet.
Comment #49
Manmohan commentedI installed the latest patch but sub-group not inheriting any content and permission.
Comment #50
Manmohan commentedI installed the latest patch but sub-group not inheriting any content and permission.
Comment #51
kaizerking commented@Manmohan can you please share zip? somehow i am not able to make this module
Comment #52
Manmohan commented@kaizerking PFA complete group module with sub group.
Comment #53
kaizerking commented@Manmohan Thanks, Installed without any glitch how ever I did not understand how to create sub group can you please give steps to create sub group please?
Comment #54
oo0shiny commentedI tried the patch in #46, but I'm getting the following error when attempting to add a subgroup to a group:
As far as I can see, it has to do with $child_group being null when passed to
but I'm still too new at Drupal 8 to figure out if this is supposed to be a valid use case or if I've done something wrong. Things seem to work if I add a check for !is_null($child_group) into the if statement.
Comment #55
CalebD commentedoo0shiny, I'm not sure how you would have triggered that error. Did you install and configure the subgroup group content type by going to the "Set available content" option for your group type(s)? Sounds like there is a bug in here somewhere that will need to be hunted down.
Updated patch to work with 1.x-dev. Still needs tests and general architectural discussion.
Comment #56
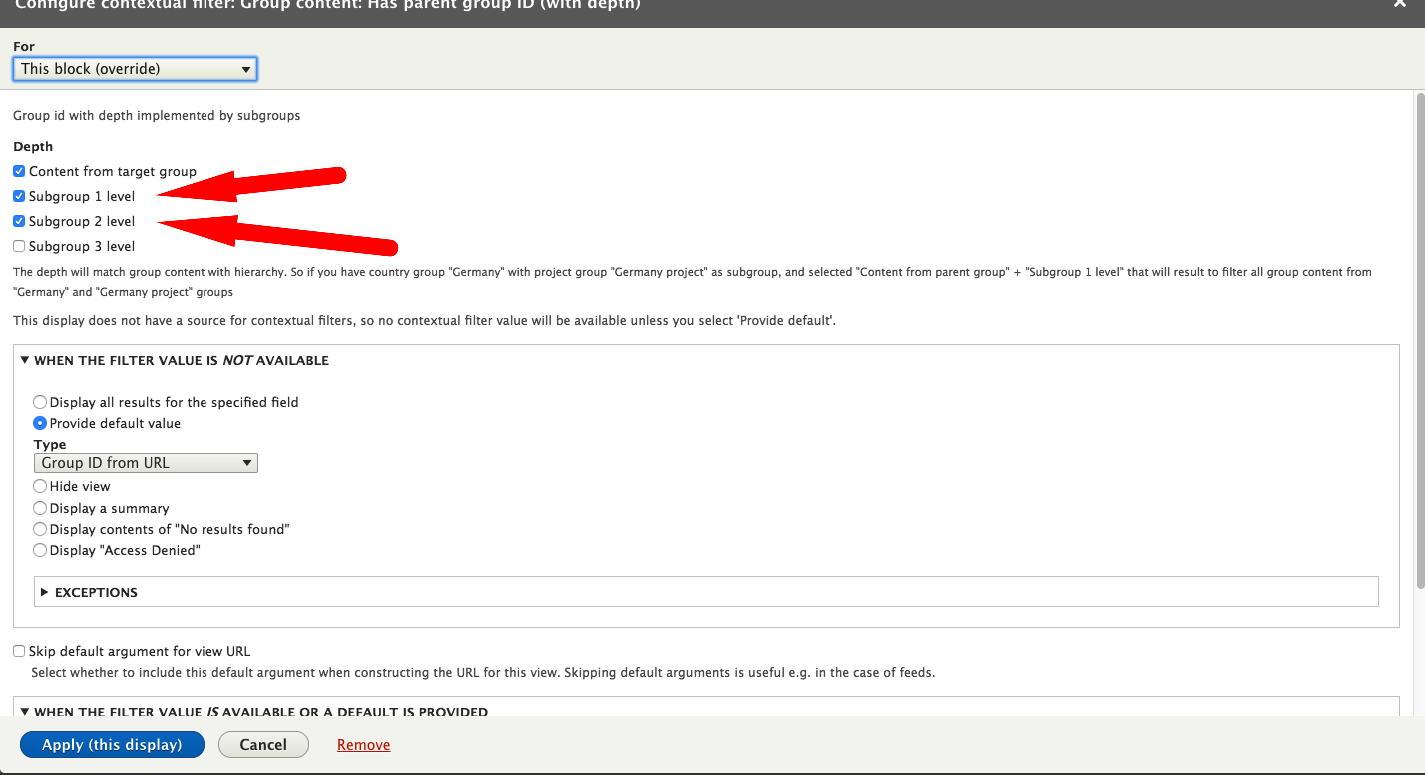
mitsuroseba commentedHere some draft version of integration ggroup with views.
Added filter to select which content to show in depends of subgroup configuration.
https://www.dropbox.com/s/annnjje56pl8y60/%D0%A1%D0%BA%D1%80%D0%B8%D0%BD...
Comment #57
mitsuroseba commentedLittle fixes.
Comment #58
Anonymous (not verified) commented@Manmohan Just installed your zip file group module replacement. Seems to be working fine, but I don't understand how to create a sub-group. Are there any instructions?
Comment #59
mhmhartman commentedAdded support for inheriting permissions from supergroups. Patch is attached. Also fixed the issues below. Please review!
Fixed this.
The parent constructor needs $temp_store_factory as well. Fixed this.
Comment #62
mhmhartman commentedFixed small mistake.
Comment #64
mhmhartman commentedIgnore my above patches. Supergroup permission inheritance will now take place in the group entity hasPermission() function.
Comment #65
mitsuroseba commentedAlso in future we should think about permission propagation.
Like upward/downward/both.
For some cases we need logic to see region content if we have country membership or vice versa if we have region membership see country content.
May be we can have this option in subgroup content enabler plugin.
Any thoughts ?
Comment #66
seanbThere is a valid case for upward/downward permission propagation. Having this as optional makes sense (in both cases). Not sure yet on the best place to put this, I will need to dive in the code a bit more. When checking access we have a group and a account. We should be able to fetch these settings from a group.
Sidenote: This could make the process of checking where the permissions are coming from pretty complex. It is easier to make a mistake so we should add some kind of warning to make sure people don't activate this without thinking about it.
Comment #67
gaydamaka commentedHi,
I apply patch #64, but plugin
GroupIdDepthwrong work.I set option in filter:

But SQL query is wrong:
Comment #69
gaydamaka commentedFix apply patch
Comment #70
gaydamaka commentedIf we remove group which is subgroup the relation is not delete. In method
removeSubgroup$group_content->getEntity()return null but$group_content->entity_idis not empty.Comment #72
gaydamaka commentedFix apply patch
Comment #73
gaydamaka commentedAdd test
Comment #76
gaydamaka commentedComment #78
gaydamaka commentedComment #82
gaydamaka commentedOption
info_textwas removed in issue.Comment #83
gaydamaka commentedComment #84
kaizerking commentedhas anyone tested #83?
Comment #85
rigoucrJust a minor fix, ensure user does not belong to a parent group before assigning it.
Comment #86
CalebD commentedI don't have time to focus on this so I am unassigning myself. However, thank you to everyone who has contributed to improve the patch!
Comment #88
spheresh commentedComment #89
spheresh commentedI decided to take the first step towards compatibility the group_graph table with the views module.
Comment #90
dang42 commentedIs the latest patch (#85) based on the code (and associated logic) added by CalebD in #45, or something else?
A quick look through the comments makes it look like multiple people were submitting multiple patches based on different starting points.
FYI - I've installed #85 against the latest dev release w/out errors. I'm testing now to see if everything works as it should, but I can't tell exactly what features to expect / test...
Thanks to everyone who has worked on this so far! I'm working on multiple project that could use subgroups and this is all looking very promising.
Comment #91
rigoucrHi @dang42.
Yes, this patch is based on the patch #45, you could verify this following the interdiffs chain.
Comment #92
mitsuroseba commentedMerge changes from #85 to our global patch (@spheresh please take a look here https://www.drupal.org/patch).
@dang42 expect/test:
1) CRUD for subgroups like content enabler plugins for other groups.
2) Permission inheritance: Now only from top to bottom.
3) Views integration: contextual argument to show selected levels of subgroup
...
Other contributors feel free to update this list.
Comment #93
seanbWe currently have a use case where there are different role that you want to propogate:
To fix this we could:
hasPermission()for a group, we should recursively check all subgroups/supergroups to check which roles the user has for each group. If the role is mapped, we should check if the role has the permission we are looking for.This leads me to believe that when you create enable a group as a subgroup, you should be able to define how to propogate each role down, and how you propogate each role up. As an example:
This way:
I will work on this next week.
Comment #94
kristiaanvandeneyndeJust letting you know that this issue is a goldmine for different points of view. When I get to a 1.0 and want to look into making subgroups part of the main module again, all of this will be really helpful. Thanks all!
Comment #95
seanbJust finished implementing inheritance as mentioned in #93. You can now specify inheritance/propagation for each installation of a subgroup. This allows a lot of flexibility (as already mentioned in a bunch of comments).
In doing this also fixed the following:
hasPermissionin\Drupal\group\Entity\Group. Much better!SqlGroupGraphStorageThings still todo:
Please test/review, feedback would be very much appreciated :)
*edit: Apparently I missed a bunch of missing new lines in the end of files. Adding this to the list.
Comment #96
seanbOne important issue comes up: You can't add a user to a group if it already inherits roles for that group. For instance, when a user is an admin, but also a regular intranet user, you want admin permissions on all groups, but member permissions on only some.
As mentioned in my last comment. The new events for the membershiploader are nice, but we probably need a way to fetch only the direct memberships too.
I see several ways to do this, but all have some limits:
Group::getMember(),Group::getMembers()andGroupRoleStorage::loadByUserAndGroup()). Not sure I'm a fan of this, but it's the best I can come up with for now.Group::getMember(). It would do the trick, but I'm not sure if we want modules to alter values in all those places.Group::getMember()we decide if the inherited members are included or not, and there is no way to change this. I think we should be a bit more flexible though. We could also provide a setting, but I could imagine situation where you want to influance this.While the patch is probably easy, it's probably best to discuss what would be the best solution first. If anyone has any other ideas, I'm very open to suggestions.
Comment #97
seanbOk last one. It seems like the inherited memberships could potentially cause issues since they are not in the database. You can't leave a group for example. The membership also can't be removed. This leads me to believe having a separate method to load the unchanged membership is probably best (after looking through the code we probably only need this for
Group::getMember()). We could mark it as internal so we don't expand the API and discourage people to use this.Patch is attached, also fixed the newlines I missed before.
Comment #98
seanbAfter testing this in an application with thousands of groups it was obvious that there were huge performance implications. The main reasons were doing queries for each path/relation. To fix this, I added static caches with the data we need to find the roles we want to inherited. This means a bit more memory is used, but is still a lot faster than all queries (5431 groups and a user being member of all of them, the request time went from 11732ms to 950ms on my local machine).
Getting the group type ID from the group content is now solved in a very hacky way :(. We need this to fetch the implied roles. This should still be fixed. Maybe it's even better to not inherit implied roles at all and remove the code?
Comment #99
jludwig commentedHey all,
I ended up using OG for rather than the Group module because of a specific problem that needed Nodes as the group type.
I still love the Group module, though, and would like to help out when possible.
For this particular problem on the OG side, we are _not_ going to attempt to solve the role inheritance problem in the module itself.
Too many people have too many opinions and there are too many use cases, that it ended up being a better use of time to give an example of how to add some custom business logic to fulfill specific inheritance requirements rather than trying to provide some generic functionality that will 100% satisfy no one's needs.
My suggestion would be:
- Make subgroups only involve posting groups into groups
- Provide some helpful APIs for subgroups
- Create a separate subgroups role inheritance module that is semi-generic; essentially just choose one of the solutions here, knowing it won't solve everyone's use case
- Label that module as an example of how to implement role inheritance, acknowledging that it is a difficult problem and that one may need to develop their own business logic for their specific need
@kristiaanvandeneynde you looked like you were flirting with this conclusion in #94. What do you say?
Comment #100
seanb@jludwig The way I currently implemented inheritance is as flexible as it comes. You can specify inheritance for every single relation between group types (up and down). This basically allows people to configure whatever they need.
The added hooks for the membership loader provide extra options to:
This leads me to believe that we have very powerful options in the current state of the patch, and enough flexibility to change the current behaviour and/or extend it. Besides that, configuring inheritance is optional.
I do agree that we can't implement every possible use case, but I think basic up/down inheritance and the custom event should cover it.
Comment #101
jludwig commented@seanB
Looking at what you provided, it does seem like the the up/down inheritance is flexible enough to fit most use cases. Great work!
I would still lean towards keeping this separated from the module that simply allows adding groups to groups to allow people wishing to implement their own business logic to do so without needing too much "duct tape" code needed to override certain parts that might be disruptive in some way for their specific use case.
We had a BoF on group role/permission inheritance at DrupalCon Baltimore, and your code looks like it can solve over half of the problems that were in that room, but if it is too closely coupled to the simple ability to add groups to groups, it may make the remaining 40% need re-implement that feature before getting to their own inheritance business logic.
On a side note, I may snag some of your code for the group inheritance stuff that BioRAFT is doing. :)
Comment #102
seanbI was using the patch in a application with thousands of groups. And while I managed to fix performance for a lot of cases, there seem to be some cases where this whole membership inheritance is just messed up.
For instance:
GroupMembershipLoader::loadByUser()we get 5.000 memberships.The solutions seems very nice, and might work very well for small numbers of groups, or if a user is only a member of a small number of groups. You could say that no user actually has to be a member of all group (since we can inherit), but since we can't actually controll that, we are pretty much screwed.
All issues I encountered were caused by messing with the membershiploader. I think if we use the inheritance only for the permissions (an not actual membership) we save us a lot of trouble.
What did I change:
I think this makes the solution a lot simpler, which might address the feedback from #101
Comment #103
johnwebdev commentedLatest patch gives an exception on installing the submodule, but seems to "work" anyway.
Drupal 8.3.2
Exception: No entity type for field type on view subgroups in Drupal\views\Plugin\views\HandlerBase->getEntityType() (line 697 of /home/dcjf1/www/core/modules/views/src/Plugin/views/HandlerBase.php).
Comment #104
jayelless commentedI have found an error with group permissions for creating subgroups. The access check in class SubgroupAddAccessCheck builds the permission string using the old permission name structure:
$access = $group->hasPermission('create ' . $group_type->id() . ' subgroup', $account);but this should be:
$access = $group->hasPermission('create subgroup:' . $group_type->id() . ' content', $account);to match the current structure of group permission names.
The attached patch fixed the problem.
Comment #105
mpotter commentedPlaying with the patch in #104. I didn't set up any mapping when enabling the ggroup module. So it's not inheriting any members of my parent space. But I can't see a way to go back and edit those role mappings. Is there a URL path for that? Or not yet implemented in the patch?
Comment #106
seanbThe roles between groups can be mapped on the page where you install / edit subgroups in a group. For example, when having a parent group type named 'department' and a subgroup type 'team', it's the path admin/group/content/manage/department-subgroup-team.
The patch currently only allows the inheritance of permissions (by mapping roles). Actually inheriting membership is another story and can lead to serious performance issues. See #102.
Comment #107
kaizerking commented#104 applies nicely without any issue thanks for the work
How ever i did not understand how to create subgroup under a group
Can some one write steps to create subgroup please
Comment #108
mpotter commented@seanB thanks, found it finally (Group Types -> select Set Available Content -> Configure for the subgroup).
I have a "Top Level" group and a "Subgroup" group. I have Member permissions in both set to Create Article. I have a "testuser" who is a member of "Top Level". I have the role mapping "MAP GROUP ROLES TO SUBGROUP ROLES" setting Member to Member.
When I log in to "testuser", they can create Articles in the Top Level group, but they cannot create anything in the Subgroup.
Are you saying that I still need to manually add "testuser" to *also* be a Member of the Subgroup? If so, that defeats the purpose of subgroups to me. Trying to implement Atrium-like functionality with Group and the whole idea is to have parent groups and putting content-creation users in the top-level parent so they don't have to be manually added to all 16,000 subgroups (stores) on the site.
I understand the issues you raised in #102, but those are exactly the issues that need to be addressed for proper subgroups. Just handling permissions without handling membership is only half the problem.
In og_subgroups we distinguished between "assigned members" and "inherited members" to deal with this (and yes, still had to fix performance issues, but got it working fine with 16,000 subgroups). I'll have to take a closer look at this patch to see if I can understand your architecture better.
Comment #109
seanb@mpotter
That shouldn't be needed? I did find I sometimes need to clear the cache? I have the exact same mapping and it seems to work for me?
I totally agree. The issue is complex though since we allow role mapping down/up. You don't just inherit membership but you actually inherit a specific role (or roles). To make it more complex you can not only inherit a role from a parent group, but also from one of your children. If we find a way to solve this I 100% think this should be added.
The biggest problem is that when you are building the list of all the users memberships (inherited or not) you need to check each and every group and fetch the related parent/subgroups for those to see if there are groups to inherit. That is a big problem when you are a member of a lot of groups. If you have some insight on how to deal with this please let me know!
Comment #110
jludwig commentedIMO the way it is doing it now is acceptable for going into the core Groups module.
I'd like to reiterate what I said in comment #99, that it may be wise to not provide a specific inheritance implementation because there are so many varying use cases for subgroups, and providing an API flexible enough to deal with even half of them would probably perform terribly.
This is one of the few examples where I think it is better to _not_ provide a complete solution and to allow developers to implement the inheritance business logic needed for their own use case.
If there is a simple example that can be added so that pure sitebuilders at least have _something_, I would suggest that it be a separate submodule and an example of how a developer can implement inheritance.
Comment #111
tdwhite commentedHi everyone, I applied the patch in #104 and while I didn't get any errors I am not able to create any subgroups. I understand this is a work in progress -- so any guidance would be greatly appreciated.
I am able to activate the Subgroups module and then configure my group type as "available content". However, attempting to create a subgroup from the group page I am directed to a page (URL: group/1/subgroup/create/mysubgroup) that simply says: "The website encountered an unexpected error. Please try again later."
The error logged is below, and I have been unable to determine where to start in addressing it:
Recoverable fatal error: Argument 1 passed to Drupal\group\Entity\Form\GroupForm::__construct() must be an instance of Drupal\user\PrivateTempStoreFactory, instance of Drupal\Core\Entity\EntityManager given, called in /home/mysite/mydomain.com/drupal8/modules/group/modules/ggroup/src/Form/SubgroupFormStep1.php on line 33 and defined in Drupal\group\Entity\Form\GroupForm->__construct() (line 33 of /home/mysite/mydomain.com/drupal8/modules/group/src/Entity/Form/GroupForm.php) #0 /home/mysite/mydomain.com/drupal8/core/includes/bootstrap.inc(566): _drupal_error_handler_real(4096, 'Argument 1 pass...', '/home/mysite/de...', 33, Array) #1 /home/mysite/mydomain.com/drupal8/modules/group/src/Entity/Form/GroupForm.php(33): _drupal_error_handler(4096, 'Argument 1 pass...', '/home/mysite/de...', 33, Array) #2 /home/mysite/mydomain.com/drupal8/modules/group/modules/ggroup/src/Form/SubgroupFormStep1.php(33): Drupal\group\Entity\Form\GroupForm->__construct(Object(Drupal\Core\Entity\EntityManager)) #3 /home/mysite/mydomain.com/drupal8/modules/group/modules/ggroup/src/Form/SubgroupFormStep1.php(44): Drupal\ggroup\Form\SubgroupFormStep1->__construct(Object(Drupal\Core\Entity\EntityManager), Object(Drupal\user\PrivateTempStoreFactory)) #4 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/DependencyInjection/ClassResolver.php(28): Drupal\ggroup\Form\SubgroupFormStep1::create(Object(Drupal\Core\DependencyInjection\Container)) #5 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/Entity/EntityTypeManager.php(187): Drupal\Core\DependencyInjection\ClassResolver->getInstanceFromDefinition('Drupal\\ggroup\\F...') #6 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/Entity/EntityManager.php(82): Drupal\Core\Entity\EntityTypeManager->getFormObject('group', 'ggroup-form') #7 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/Entity/EntityFormBuilder.php(44): Drupal\Core\Entity\EntityManager->getFormObject('group', 'ggroup-form') #8 /home/mysite/mydomain.com/drupal8/modules/group/modules/ggroup/src/Controller/SubgroupWizardController.php(131): Drupal\Core\Entity\EntityFormBuilder->getForm(Object(Drupal\group\Entity\Group), 'ggroup-form', Array) #9 [internal function]: Drupal\ggroup\Controller\SubgroupWizardController->addForm(Object(Drupal\group\Entity\Group), Object(Drupal\group\Entity\GroupType)) #10 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/EventSubscriber/EarlyRenderingControllerWrapperSubscriber.php(123): call_user_func_array(Array, Array) #11 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/Render/Renderer.php(574): Drupal\Core\EventSubscriber\EarlyRenderingControllerWrapperSubscriber->Drupal\Core\EventSubscriber\{closure}() #12 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/EventSubscriber/EarlyRenderingControllerWrapperSubscriber.php(124): Drupal\Core\Render\Renderer->executeInRenderContext(Object(Drupal\Core\Render\RenderContext), Object(Closure)) #13 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/EventSubscriber/EarlyRenderingControllerWrapperSubscriber.php(97): Drupal\Core\EventSubscriber\EarlyRenderingControllerWrapperSubscriber->wrapControllerExecutionInRenderContext(Array, Array) #14 [internal function]: Drupal\Core\EventSubscriber\EarlyRenderingControllerWrapperSubscriber->Drupal\Core\EventSubscriber\{closure}() #15 /home/mysite/mydomain.com/drupal8/vendor/symfony/http-kernel/HttpKernel.php(144): call_user_func_array(Object(Closure), Array) #16 /home/mysite/mydomain.com/drupal8/vendor/symfony/http-kernel/HttpKernel.php(64): Symfony\Component\HttpKernel\HttpKernel->handleRaw(Object(Symfony\Component\HttpFoundation\Request), 1) #17 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/StackMiddleware/Session.php(57): Symfony\Component\HttpKernel\HttpKernel->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #18 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/StackMiddleware/KernelPreHandle.php(47): Drupal\Core\StackMiddleware\Session->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #19 /home/mysite/mydomain.com/drupal8/core/modules/page_cache/src/StackMiddleware/PageCache.php(99): Drupal\Core\StackMiddleware\KernelPreHandle->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #20 /home/mysite/mydomain.com/drupal8/core/modules/page_cache/src/StackMiddleware/PageCache.php(78): Drupal\page_cache\StackMiddleware\PageCache->pass(Object(Symfony\Component\HttpFoundation\Request), 1, true) #21 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/StackMiddleware/ReverseProxyMiddleware.php(47): Drupal\page_cache\StackMiddleware\PageCache->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #22 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/StackMiddleware/NegotiationMiddleware.php(50): Drupal\Core\StackMiddleware\ReverseProxyMiddleware->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #23 /home/mysite/mydomain.com/drupal8/vendor/stack/builder/src/Stack/StackedHttpKernel.php(23): Drupal\Core\StackMiddleware\NegotiationMiddleware->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #24 /home/mysite/mydomain.com/drupal8/core/lib/Drupal/Core/DrupalKernel.php(656): Stack\StackedHttpKernel->handle(Object(Symfony\Component\HttpFoundation\Request), 1, true) #25 /home/mysite/mydomain.com/drupal8/index.php(19): Drupal\Core\DrupalKernel->handle(Object(Symfony\Component\HttpFoundation\Request)) #26 {main}.Perhaps I have made a simple mistake? I made sure to install a fresh Drupal, version 8.3.4 and encountered the same issue. I made sure to apply it against 8.x-1.x-dev dated 2017-Jun-06.
Here are my web server details in case relevant: Apache/2.2.32 (Unix) mod_ssl/2.2.32 OpenSSL/1.0.1e-fips mod_bwlimited/1.4 PHP/5.6.30
Thank you
Comment #112
johnwebdev commentedSmall review:
Can we have a better machine name rather than page_1?
Use []
Use []
Use []
EntityManagerInterface is deprecated.
EntityManagerInterface is deprecated.
Should be able to just use $result->fetchAll(); here instead?
Comment #113
mgalalm commentedI have the same issue like comment #112, I modified the patch in #104 slightly to fix this issue.
Comment #114
mgalalm commentedJust fixing problem with last patch.
Comment #115
seanb#112 Fixed 1, 2, 3, 4 ,5
Added some small performance improvements.
Also added missing interdiff between 104-114 for easier review.
Comment #116
kaizerking commented114 & 115 both patches are breaking the site
PHP Fatal error: Call to a member function get() on null in C:\\Program Files (x86)\\Ampps\\www\\social2\\core\\lib\\Drupal\\Core\\Session\\SessionHandler.php on line 76
PHP Stack trace:
PHP 1. session_write_close() UNKNOWN?:0
PHP 2. Symfony\\Component\\HttpFoundation\\Session\\Storage\\Proxy\\SessionHandlerProxy->write() UNKNOWN?:0
PHP 3. Drupal\\Core\\Session\\WriteSafeSessionHandler->write() C:\\Program Files (x86)\\Ampps\\www\\social2\\vendor\\symfony\\http-foundation\\Session\\Storage\\Proxy\\SessionHandlerProxy.php:77
PHP 4. Symfony\\Component\\HttpFoundation\\Session\\Storage\\Handler\\WriteCheckSessionHandler->write() C:\\Program Files (x86)\\Ampps\\www\\social2\\core\\lib\\Drupal\\Core\\Session\\WriteSafeSessionHandler.php:75
PHP 5. Drupal\\Core\\Session\\SessionHandler->write() C:\\Program Files (x86)\\Ampps\\www\\social2\\vendor\\symfony\\http-foundation\\Session\\Storage\\Handler\\WriteCheckSessionHandler.php:89
Uncaught PHP Exception Drupal\\Component\\Serialization\\Exception\\InvalidDataTypeException: "Unable to parse at line 81 (near " arguments: ['@entity_type.manager', '@current_user', '@event_dispatcher']")." at C:\\Program Files (x86)\\Ampps\\www\\social2\\core\\lib\\Drupal\\Component\\Serialization\\YamlSymfony.php line 39, referer: http://localhost/social2/admin/modules
its drupal 8 fresh install
Comment #117
seanbCan't reproduce this? The stack trace also doesn't show anything related to group or ggroup modules? Are you sure it's caused by this patch?
Comment #118
seanbDid break something else, it is time to start adding a bunch of tests...
Comment #119
kaizerking commentedAfter applying#118
Enabling gives WSOD with the message : The website encountered an unexpected error. Please try again later.
Server log says:
Uncaught PHP Exception Exception: "No entity type for field type on view subgroups" at C:\\Program Files (x86)\\Ampps\\www\\social2\\core\\modules\\views\\src\\Plugin\\views\\HandlerBase.php line 697, referer: http://localhost/social2/admin/modules
Comment #120
seanbI can reproduce the issue with the view. Will try to fix that asap.
Comment #121
seanbOk fixed the WSOD. There is another issue though. We can't filter the subgroup view to show only subgroup group content. There is no plugin type available. You can add these after you actually create group types and install subgroups for the group types.
I think there should be a filter for plugin type 'subgroup'. So this still needs some work.
Comment #122
kaizerking commentedAs of now #121 workings goodl..
Comment #123
seanbUsing migrate to import groups and subgroups, I noticed the graph got messed up after changes in the source data. I'm assuming this is an error on my part, but this got me thinking that the only time the graph is properly created or check is when adding subgroup content. Since the graph is a form of caching for the relations, it would be nice to be able to recalculate the graph.
The code below does exactly this, not sure how to fit it in the module. Maybe a configuration page that adds a button to do this?
Comment #124
ericras commented1. On /group/%/subgroups I'm seeing all of the group's content listed - nodes, users, menus. **EDIT: Is this what #121 is referencing?
2a. In src/Plugin/GroupContentEnabler/Subgroup.php all of the permissions should be for "entity" not "content". They should be like
$permissions["create $plugin_id entity"]. "entity" is for new creation and "content" is for relating.2b. Need to set the 'create_mode' flag that distinguishes creating/relating as is done in gnode. (Also see #2881769: group/{group}/node/create uses the permissions of group/{group}/node/add). In SubgroupRouteProvider.php:
Comment #125
ericras commentedHere's an update that addresses point two in the last comment. (I'll once again point out that permissions specificity relating to creating vs relating is broken per #2881769: group/{group}/node/create uses the permissions of group/{group}/node/add)
Comment #126
ericras commentedAn update to #125 to fix the Edit permissions machine name: it should be "update" not "edit".
Comment #127
seanb#124.1 Yep, that's what 121 is about. Not sure how to fix?
#126 Nice one. Just ran into this myself. Improved the patch a little to fix the ordering and the description of the relations permissions. Also fixed weird references to a
create $name grouppermission that doesn't seem to exist. Not sure why it was there?Comment #128
jts86 commentedAdded support for parent group tokens for Subgroups. Based in https://www.drupal.org/node/2774827.
Comment #129
jts86 commentedUnchecking the " 2-step wizard" option in a subgroup content plugin seems to have no effect... the second screen still appears regardless of the value of that option. This patch aims to fix the problem.
Comment #130
parijke commentedApllied patch #129
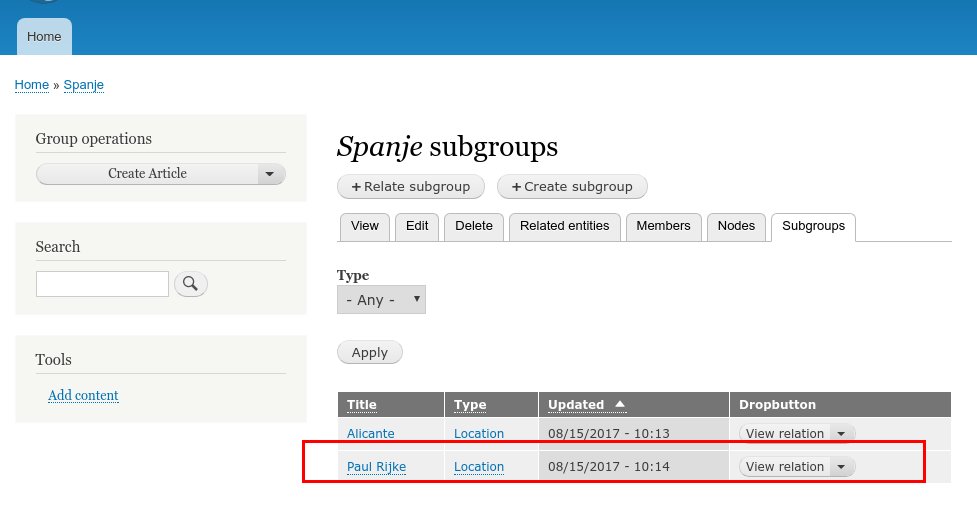
While creating subgroups, In the subgroup tab I see myself show up as a subgroup... That I did not expect to happen?
Just created a location group type
Activated gnode (article) and ggroup (location) on it
created group Spanje
in group Spanje created subgroup Alicante
Comment #131
idebr commented@parijke in #130
The missing filter on the subgroups pages to display only group content of the type 'subgroup' was identified in #121 and #124.1 as well
Comment #132
parijke commented@idebr you're absolutely right.... punish me for my lazyness (didn't read the whole thread)
Glad it is in vision though
Comment #133
Anonymous (not verified) commentedHello,
My config is: Ubuntu 16.04, PostgreSql 9.5, Drupal 8.3.7 Group 8.x-1.0-rc1, Patch #129, with Group an SubGroup modules Installed.
Have Created 2 groups types Country and Region. SQL Error when creating a Region in a Country (see screenshot)
I guess it is because I am using PostgreSql.
All the best,
Comment #134
idebr commentedFixed an issue where inherited group roles from the supergroup were written to the static cache of inherited subgroup roles, causing incorrect permissions.
Comment #135
nikolabintev commented#129 works fine for me. The only issue I experienced is that no matter if I'm creating new group entity or relating an existing one, the same permissions is used for access check, which doesn't allow us to restrict the user to relate an existing entity in group by using Group permissions table.
Here is a patch that fixes the issue
Comment #136
idebr commented@nikolabintev #135
Your patch does not include the changes in #134. Can you post a new patch based on #134?
An interdiff would also help for reviewing your changes. You can find info on how to generate an interdiff at https://www.drupal.org/documentation/git/interdiff
Comment #137
nikolabintev commented@idebr I'll remove patch #135 as it is related to another issue: https://www.drupal.org/node/2881769
Comment #138
mitsuroseba commentedFix issue.
Method getPath tried get directAncestors from group which doesn't have those.
Comment #139
arosboro commentedI've updated Subgroup.php with a patch that fixes a harmless warning about parent_role_mapping and child_role_mapping indexes being undefined for the default values.
Comment #140
arosboro commentedI jumped the gun there, it looks like a sanity check is required after submitting the form and going back to the Group Content Types overview.
Comment #141
arosboro commentedRegarding #121 and #124.1, I have updated the view to properly display only subgroup content, and fixed the dropbutton links.
Comment #142
arosboro commentedComment #144
maticb commentedTested patch #141 and quickly came across 2 issues, but they may have already be mentioned, as I might have missed it in all of the comments above :)
- When navigating to the "subgroups" tab on any group it always says "An illegal choice has been detected. Please contact the site administrator.", because the "- Any -" option is selected, but not working.
- When you press "Create subgroup" you cannot select group type you are automatically placed onto an add form, instead of the group type selection form.Other than that I think it's in good shape, but didn't do much in depth testing yet, as I am currently looking for options in my use case.
EDIT: I have realized now that I have to install content plugin for each group type, to be able to add it as a subgroup.
Comment #145
ryandekker commentedWas running into an issue where a user in a parent group could view/edit/delete a subgroup they weren't a member of. Looks like these permissions didn't do anything: "$operation any/own $plugin_id entity" (example:
view any subgroup:<subgroup_type> entity).I basically cloned and tweaked what gnode.module is doing in
gnode_node_access(). Tested and this is working for me. (I haven't test the Views work from #141.)Comment #147
Alumei commentedIt might be a little late to ask, but:
Might it be actually easier to propagate roles instead of permissions for a first access related solution?
My thinking:
* Create outsider roles for group-types based on configured group-type as content relations in other types
* Go up the group nesting from the corresponding bottom, selecting the first actual membership to be found
* Use that membership to select appropriate outsider permissions in case the use is not a member
Even it does not make sense in this context I would still propose separating the permission-bubbling so something like the above could be used instead.
Comment #148
lukedekker commentedFound an issue in this patch. From the subgroups page of a group, the edit and delete operations for each row point at the parent group, not the subgroup.
This means that attempting to delete a child entity from this interface results in the deletion of the parent instead.
Comment #149
seanbAdded a fix for #2933819: getPermission does not convert plugin label to string properly to the patch.
About #145:
This could be caused by the membership inheritance. If you set your groups up to inherit a role from a parent/child, you could get access to groups you are not actually a member of. This is exactly the point of the current patch and I don't think the
ggroup_group_access()should be needed.Comment #150
seanbWhen using large amounts of subgroups with inheritance we still noticed a significant decrease in performance. This was even worse after upgrading to RC2.
I think I found a way to prevent calculating the inherited roles for groups on every request by building a cache with all possible direct/indirect relations between groups and the roles that are inherited. The cache is invalidated and rebuilt when subgroups are added or removed.
Please let me know if you find any issues.
Comment #152
seanbOn a sidenote, I also used the patch in #2878389: Add static cache to gnode_node_grants. Without that patch, overview are still a bit slow. The function
gnode_node_grants()adds a lot of calls to$group->hasPermission().Also not sure why PHPLint fails on the splat operator?
Comment #153
seanbFixed a PHP warning and corrected small doc error.
Comment #154
arosboro commentedggroup also has the same issue found at #2793621: Upload files when adding content to group don't work well, which can be solved with the same solution as #12 applied in that thread.
Comment #155
paul kim consulting commentedHi @seanB,
I tried your patch in #150, and have set the role inheritance correctly between group and subgroup, but I'm not seeing the inheritance working correctly.
My group is called "State" and my subgroup is called "District". I have 3 different roles for both groups: Program Manager, Team Member, and Guest. Any role in "State" should have Guest access to the "District".
Here is how my District subgroup content plugin is configured:
Whenever I try to access a given permission for a "District" with a user that has "Program Manager" role in the "State", I don't get the permission inheritance as defined by the configs of the content plugin. But if I manually add that role for the "District" to the user, it works fine.
Am I missing something?
Comment #156
seanbAdded the changes from #2793621-12: Upload files when adding content to group don't work well as suggested in #154.
Also fixed another issue with merging group roles in
GroupHierarchyManager::getInheritedGroupRoleIdsByUser().@ #155 Paul Kim Consulting, it seems you are doing everything right. If you are able to debug the issue and provide some more insight that would be really helpful!
Comment #157
dylan donkersgoed commentedSame issue as #155 here. Seems like this line in GroupHierarchyManager is the culprit:
the role map and the final result need to be flipped as well.
Comment #158
hlopes commentedI think there's an issue here, as the ggroup-form messes up the form id, meaning one can't implement hook_form_FORM_ID_alter.
Comment #159
hlopes commentedPatch & interdiff attached.
Comment #160
ozvalue commentedI have been able to "git apply -v" the .156 patch to the group-8.x-1.x-dev module with only whitespace errors warning. I then package up the new group module as a .tar.gz and use that to install into a clean Drupal 8.5.4 installation.
I then enable (within the administrations 'extend' menu item) the modified group module into a clean Drupal installation which is installed with the latest 64 bit bitnami LAMP stack.
Enabling group and 'group node' causes no problems.
When I try to enable subgroup I get the message:
"The website encountered an unexpected error. Please try again later."
on a White Screen Of Death.
The last lines at: apache2/logs/error_log show
"[Wed Jun 20 13:54:30.453360 2018] [php7:notice] [pid 13439] [client 127.0.0.1:52768] Uncaught PHP Exception Exception: "No entity type for field type on view subgroups" at /opt/lampstack-7.1.18-1/apps/drupal/htdocs/core/modules/views/src/Plugin/views/HandlerBase.php line 711, referer: http://localhost/drupal/admin/modules"
PHP Version:7.1.18 MySQL Version:5.7.22
This appears to be the same error from #119 except that the HandlerBase.php has gone from line 697 to 711. Yet, this was meant to have been fixed at #112
Regardless of the above, when I now check the enabled modules (within the administrations 'extend' menu item) it shows that subgroup has been enabled
I have redone the above
but using group-8.x-1.0-rc2 with the later 157 patch
and group-8.x-1.x-dev with the latest 158 patch
but in each case I got the same result.
Before using this 64 bit computer I tried to implement it on an old 32 bit laptop with older LAMP software but I had the same problems.
Are other people getting the same as this?
Is there anything I can do to not get this?
Many thanks
Comment #161
jordik commentedApplied patch from #159, it installed well and I could link groups and subgroups.
The roles and permissions inheritance and propagation though DID NOT work at all.
After debugging, I reverted the changes from #155 (no additional array flips) and voila - the permissions worked!
Why are those additional array flips of the role_map necessary at all?
Comment #162
sketman commentedBug: when group is deleted, it still remains listed in "Content" tab, as a Subgroup. Hitting the "Install" button next to the deleted group throws error...ofcourse:) Please see atached screenshot.
I have installed a patch #159.
Comment #163
sketman commentedI wanted to unistall the entire Group suite. When uninstalling Group Node and Subgroup modules, I got error:
Site is now unaccessible. Drush cr does not help, neither restarting Apache.
Apache logs say:
Any thoughts please?
Comment #164
floydm commentedThis is 156 rerolled to pick up the translation of the parent group in the tokens, similar to:
https://www.drupal.org/project/group/issues/2774827#comment-12835463
With this patch applied one can use a path alias like:
[group:group:title]/[group:title]And get the parent and the child in the same language.
Comment #165
floydm commentedSorry attached 156 again instead of new patch 164.
Comment #166
martijn de witChanged status for testing and added a test for #165
Comment #169
jnicola commentedWe've got something going like this for our configuration already. Curious how this would compare. It's custom written for a particular set of groups, and menus in groups.
Comment #170
lukedekker commentedI've been running the patch from #165 on a project with a large number of groups (about 50K). Our structure is really simple with just groups and subgroups. The method of loading the entire groups_graph structure and using that for role inheritance just doesn't work for a project with our type of structure/size. Operations dealing with groups use a debilitating amount of memory (peaking around 900M) and take an extraordinary amount of time (no duh).
I've created an alternate method for loading group hierarchy that loads only one group at a time. I realize that there are potential issues with other projects with a deeper group structure, but at least for our use case, we've seen a dramatic improvement in performance. I also added caching on the hierarchy mapping, so that we're only hitting the database when we have to and only for the data that we need.
Not saying that this is the way to do this, but I think it's a step in the right direction. The existing solution just doesn't scale well enough for large projects. I haven't dug into the role inheritance logic, but I have a feeling that this issue is really just revealing another performance issue further up the chain.
Comment #171
martinma commentedApplying patch #170 worked, but enabling modul I get fatal error and following message in dblog:
Comment #172
webadpro commented@MartinMa, I had the same issue, until you actually create a group type. I'm testing using Opigno_LMS.
Comment #173
martijn de witDon't forget to change the issue status when you commit a patch. Otherwise tests will not run :)
Added a test manually.
Comment #174
lukedekker commented@Martijn de Wit Ah thanks for that. Totally forgot.
I've kept working on this and made a similar change to the GroupRoleInheritance service, allowing mapping to be built for one group at a time. Also fixed a few bugs in the last patch.
Again to reiterate: I don't think this is the correct solution. I'm just dipping my toes into the inner workings of ggroups. I'm happy to keep pushing this along, but I would super appreciate some feedback from everyone. I'm basically just hacking ggroups so that it isn't a total memory hog for my use case. :/
Comment #176
floydm commentedWe're building a distro with subgroups using the patch from #165. We have a demo content module that creates a bunch of test groups, then behat tests that verify our group content and relationships.
Testing either the patch from #170 or #174, I'm getting a lot of failures. In particular it appears to be related to the GroupHierarchyManager. Code like
$subgroups = \Drupal::service('ggroup.group_hierarchy_manager')->getGroupSubgroups($group->id());gets an empty array back when there are valid subgroups.
I've inserted some cache clearing just in case it was a caching issue, but that doesn't appear to make a difference.
For now we're sticking with #165.
Comment #177
floydm commentedAttached is a reroll of the patch from #164 with a better validation. This is following alex.rutz's suggestion on a similar change on 2774827.
Comment #179
lukedekker commented@floydm Awesome, thanks for the feedback.
Holy cow. I had a huge bug in the loadMap function.
This works on the SECOND check of any page request, but not the first.
I also found a bunch of places where I was misspelling descendants (decendants).
Anyways, Fixed both of those issues and now you can load the subgroups on the first try :)
@floydm, would love for you to test this out and see if it fixes things for you.
Also I forgot to reroll with your last patch, so if anyone wants to go for it. Otherwise I'll hit that next go around (as I'm sure there will be one).
Comment #180
lukedekker commentedAlso, I lied. It doesn't work on the second try. Honestly, I have no idea how this was working for me....
Comment #181
floydm commented@lukedekker My tests are still failing with the patch from #179 but failing differently now. Which is progress. :)
With #177 I am able to see the subgroups and supergroups, but user permissions aren't cascading.
Our scenario has:
Parent group with group content (nodes).
Child group which users are members of.
The members of the child group inherit access to view the content in the parent group by virtue of parent/child group role mapping.
This works on #177 but not #179 (Access Denied).
Comment #182
lukedekker commentedOk. Here is an updated patch (again). I believe that it addresses the issues you were having @floydm.
I also found yet another area where a permissions check was loading every single group_content entity of a specific plugin. (This time it only took up about 600MB, yay.)
Anyways, fixed those, also fixed a caching issue that I found.
Thanks for helping me test this!
Comment #183
floydm commentedHey @lukedekker! I'm on holiday but don't want to keep you hanging, so I applied your latest patch and ran my tests. I went from 4 failing previously down to 2 failing now.
The errors seem to be related to role access inheritance still. For example, when I'm accessing the parent group as a member of the child group, I'm still getting "Access Denied" and a screen full of notices like:
I probably won't have a chance to chase this down in any more detail until after the holidays but I hope this helps you out.
Comment #184
lukedekker commented@Floydm, can you confirm that there is a valid subgroup for your group id 1?
I believe I've run into that issue before when running patch from #164.
Currently, my inclination from past behavior and looking at the logic in place is that we need better handling for this situation, but there is no serious issue in the logic here.
Comment #185
steveworley commentedHey @lukedekker I was just testing your latest patch and ran into something that I thought might be worth flagging. I needed to create a hierarchical list of subgroups for navigation. I couldn't find this functionality but started looking through GroupHierarchyManager and SqlGroupGraphStorage and found that the functionality is pretty much there.
One thing I was having trouble with was loading the group mapping from cache- the merge of the mapping data didn't work as I expected, so I just wanted to raise this.
This has issues if you load multiple group mappings in a single request. I'll try and explain; I set up a pretty simple hierarchical structure I had 3 levels of subgroup nesting. If you loaded the first in the hierarchy it would show all leaf nodes correctly. If you stepped down, you would correctly see the remaining subgroups but you wouldn't see siblings.
The output I was looking for was something like:
If I was on the Subgroup 1 page - I would see only its children, if I was on Subgroup 1A I would see the full tree similarly to if I was on the parent of Subgroup 1 I would see the full tree as well.
I was loading the ancestors of the current term to get the most senior in the hierarchy which would do an initial load and set the mapping in SqlGroupGraphStorage. When I was to load descendants to build the tree it didn't merge the new mappings as I was expecting. Some pseudo code to show the state:
Array replace results in the result that I was expecting and it didn't seem to affect other functionality.
Comment #186
lukedekker commented@steveworley you raise a great point. That merging logic is not working the way that we really need it to.
However, I think the fix that you're suggesting will actually cause the same problem you're describing if it is applied in the opposite order.
So this works fine if you're loading your projects from child to parent, but causes the same problem in the opposite direction. I can't think of any baked-in methods that will do what we need here, so we may have to create a custom merger to handle this. Any better ideas anyone?
Comment #187
steveworley commentedYeah that's a good point. I think a custom merge function will be required. I looked into
NestedArray::deepMergeArray(). Which on the surface looks to work but because the mapping at lower levels has arbitrary keys we run into some potential issues.When creating the mapping we might be able to create the second array with keys that match the group id? Something like:
That would make the merge look more like:
And then we could level the NestedArray merge functionality.
Comment #188
steveworley commented@lukedekker I also ran into the notice mentioned in #183.
It looks like the role inheritance getSubgroupRelationConfig is called multiple times with different group IDs but the subgroup relation is only cached once for a single group ID.
For example my page calls that method 3 times with: 13, 12, 13.
This block is only evaluated once:
because we set subgroupRelations on the first call and because the query is restrictive to the first gid that is received. $this->subgroupRelations[$group_id] will only ever be set for the first group_id that method is called with.
Comment #189
lukedekker commented@steveworley great idea to convert those to associative arrays. I like that structure a lot better (I converted
$this->mapping[x]to be associative as well).Also, once you pointed out where the subgroupRelation stuff was failing, it became painfully obvious why that was failing. Once any subgroup relation is fetched, it's statically cached. Meaning that
if (!$this->subgroupRelations) {will always be false.Attached is a patch that adds the custom merge logic we talked about and resolves the subgroup relation config issue.
Huge thanks for the help!
Comment #190
mmjvb commentedAssuming you want your patch tested !
Comment #194
steveworley commentedAwesome! I'll patch and test that out but it looks good from the diff! :D
I just had a quick question about the group role inheritance and was wondering if you might be able to explain the intent and make sure that I'm understanding it correctly. The inheritance is for the permissions configured for each role; if I have a "Content Creator" role its permissions will be shared between each subgroup.
I'm looking to have the membership inherit as well (eg. you can add a user to the most senior group and it will have the same access to all subgroups).
Am I right in assuming it's the roles that are inherited and membership needs to be manually updated?
Comment #195
lukedekker commentedGah, always forget to change the status. Thanks @mmjvb!
@steve it's actually a really clever system if a bit unintuitive. Props to whoever thought it up and implemented it.
By default, there is no permissions inheritance between groups and subgroups. What you need to do is hit the config page for the plugin between the parent type and child group type. That page allows you to map roles between the two. Basically you would configure a relationship between the "Admin" role on the parent group to the "Owner" role on the child. That means that regardless of whether the admin is an owner of the child, they will have the permissions of the Owner. And you can do the same thing in the opposite direction.
The hardest part is finding the page. I stumbled upon it accidentally - lucky for me :). Hope that helps?
Comment #196
steveworley commentedAwesome! Thanks so much for that, that's pretty much exactly what I needed.
Was just noticing the tests failing; it's failing because php 5.5 doesn't support splats so php -l thinks theres a syntax error. I think we just might need to rerun the test against a newer version of php; should we add the php version constraint to the modules composer.json to make sure that people know 5.5 isn't supported?
Other than that the latest patch is working just fine!
Comment #197
lukedekker commentedJust reran against PHP 7 and passed! There's still a bunch of coding standards warnings that ought to get resolved before we consider this RTBC. (Some of which are definitely from me! :/ )
I'm starting to feel that we may be getting close to a production-ready version.
Comment #198
mmjvb commentedAs per 195,196,197 set to Needs work
- Coding standards
- PHP 7 requirement
Comment #199
lukedekker commentedK, Did a bunch of coding standards cleanup and added the PHP 7 dependency. Let's see how this goes.
Comment #201
lukedekker commentedAaannnd fixing the issue with my PHP version constraint.
Comment #203
lukedekker commentedA few last coding standards. and I think we're good to go!
Comment #205
lukedekker commentedAccidentally dropped the composer stuff in the last patch...
Comment #206
Andrei Tyuhai commentedGot an exception while installing the subgroup module patched with #205:
Exception: No entity type for field type on view subgroups in Drupal\views\Plugin\views\HandlerBase->getEntityType() (line 712 of /app/web/core/modules/views/src/Plugin/views/HandlerBase.php).Notice: Undefined index: gc__group in Drupal\views\Plugin\views\HandlerBase->getEntityType() (line 702 of core/modules/views/src/Plugin/views/HandlerBase.php).Comment #207
lukedekker commentedBased on my testing, this error only occurs if there are no existing group types when installing the subgroup module. It's triggered by the missing
gc__grouprelationship used inggroup/config/optional/views.view.group_members.ymlwhich is provided by groups. I'm guessing we just need an extra dependency on that config.Although I'm wondering if it would be better to force groups to define the gc__group relationship in
src/Entity/Views/GroupContentViewsData.phpAny good ideas here?
Comment #208
dangur commentedRelating nor creating subgroups was working with PostgreSQL. This adds a condition for the parent and child group graph.
Comment #211
jedgar1mx commentedIs there a estimated date for this release? or any suggestions on how to achieve sub-grouping like control with the current `group` release.
Thanks
Comment #212
Quicksaver commentedPatch 208 was failing to apply on 8.x-1.x, because of 3028343 and 3026897
Rerolled it as I need it for a project that relies greatly around this functionality, but I'm having trouble creating an interdiff because of the huge amount of changes in the latest commits there. So changes are:
- composer.json and group.services.yml : simple merge conflicts
- moved permission_event logic from src/Entity/Group.php to src/Access/GroupPermissionChecker.php :: please verify if the logic is still valid!!
Looks like it's working so far on my end, although I see some issues that I can't tell if they're due to my patch or if they existed already:
- First going to the subgroups page, I get an "An illegal choice has been detected." on the "Type" filter and no groups appear until I click on Apply to re-filter the groups list.
- "Type" filter in the subgroups page shows all existing group types even though I've only enabled one in a group.
- The autocomplete of the relate (add) subgroup page does not work (I never have any choices).
- When I create a new subgroup, I'm directed to an "Access denied" page (the group page) if that group type is not setup to either add the current user as a member or if external members cannot see it. Maybe directing to the subgroups page you were in before could be safer?
Comment #213
lukedekker commentedAwesome! Thanks for the re-roll. It's a huge help :) I'm not surprised that you're running into a few issues with the UI. As far as I can tell, nobody has touched the user-facing issues in about a year!
Your patch applies like a dream, and I'm excited that we're getting closer.
It does look like a few of the tests are failing now, so we'll need to address those, but hopefully, we can get this RTBC once we get the UI and testing issues sorted out.
Comment #214
Quicksaver commented"The autocomplete of the relate (add) subgroup page does not work (I never have any choices)."
Just leaving this here: this looks like a permissions issue, it works if I'm adding the group as the site admin (user 1), but not if it's any user with the appropriate group permissions.
Comment #215
dangur commentedWith regard to the "An illegal choice has been detected." issue, adding something like this should resolve:
Might be slick one day to automatically detect if there is only one type and if so, select that type.
Comment #216
dangur commentedRe-rolled for Drupal core version bump to 8.6.
Comment #217
dangur commentedComment #218
lobsterr commentedFixed broken tests
Comment #219
jedgar1mx commentedIs the patch working on D8.7 or only 8.8?
Comment #220
martijn de witAdded a test so we wil see :)
https://www.drupal.org/pift-ci-job/1250184
Comment #221
jedgar1mx commentedAwesome!!!
Comment #222
webadpro commentedThings are looking great guys! Awesome work.
Comment #223
Quicksaver commentedJust to mention access grants to nodes within a groups hierarchy are not yet fully defined. For example, in my case I had to write a hook_node_grants() that would set the appropriate grants based on a group's subgroups and parent groups.
I haven't added a new patch with it as I wrote it with my single use-case in mind and I don't know if that's the proper way to go for this, it just happened to work for my very specific (and a bit simple) group hierarchy setup.
Comment #224
dan_billingsleyI'm trying to use this patch as the subgroup functionality is a critical piece for a site I'm looking to build. As soon as I add the patch I start having errors any time I access a group. It seems that the EventDispatcherInterface is not getting injected in the GroupPermissionChecker constructor.
Any ideas where to go from here?
ArgumentCountError: Too few arguments to function Drupal\group\Access\GroupPermissionChecker::__construct(), 1 passed in C:\SoftwareDev\wamp.net\sites\lifestylelinkv2\core\lib\Drupal\Component\DependencyInjection\Container.php on line 269 and exactly 2 expected in Drupal\group\Access\GroupPermissionChecker->__construct() (line 38 of modules\contrib\group\src\Access\GroupPermissionChecker.php).
Comment #225
lobsterr commentedSmall fix for subgroups view to avoid "An illegal choice has been detected. Please contact the site administrator" warning
Comment #226
lobsterr commented@dan_billingsley
We are constantly using this patch in our project and It works correctly.
Can you check your service file group.services.yml? It should contain the next config
Maybe a cache issue ?
Comment #227
jcmartinezSo far, I can create subgroups through the admin pages; however, when I try to create them via migration something is not working right.
I've posted on https://www.drupal.org/project/group/issues/3060352, but I thought that I should mention it here because there may be something missing in the code of this sub-module.
Comment #228
jedgar1mx commentedI tried
#225onDrupal 8.7.2and it errored out.Comment #229
mmjvb commentedNo surprise there with a patch for D8.8 !
Comment #230
jedgar1mx commentedI tried #218 as well which had
8.7passing.Comment #231
mmjvb commentedSorry, meant to say: patch for D8.8 failing !
Wonder why it didn't run for D8.7, the current active version!
Comment #232
jedgar1mx commentedGroup: 1.0.0-rc3Drupal 8.7.3I keep getting this error:
Comment #233
jedgar1mx commentedHere is the verbose output:
Comment #234
jedgar1mx commentedI checked some of the files just to make sure that the patch didn't get commited to the new release but the changes were not there. 🤔
Comment #235
kristiaanvandeneyndeYeah, I basically had two choices here:
I went with option A. I hope you can forgive me ;-)
Comment #236
jcmartinezAs being said above, with the release of 8.x-1.0-rc3, the patch #225 broke. I finished applying the code from the patch manually, and so far things are working for me.
Attached is a new version of the #225 patch that includes my manual tweaks to make Subgroups available on 8.x-1.0-rc3.
Comment #237
jedgar1mx commentedThanks @jcmartinez for the update. @kristiaanvandeneynde I undertand the need to get the release out I was just trying to make sure it wasn't just me.
Comment #238
jcmartinezIf someone could tell me in plain English (or Spanish) what does it mean "Ancillary require failure", I'll be happy to try fixing the #236 patch.
The "Ancillary require failure" feedback from testing sounds a bit cryptic to me; although, it could be just my English.
Comment #239
it-cru@jcmartinez: I think this failure message occurs, because in the patch is php 7.0 or higher required and the test currently try to test with PHP 5.6.
[InvalidArgumentException]
Package drupal/group at version dev-ancillary-branch as dev-1.x has a PHP requirement incompatible with your PHP version (5.6.37)
Comment #240
lobsterr commentedI have found a few edge cases when subgroup inherits roles from the parent group.
We can't correctly inherit roles for Anonymous and Outsider users.
These two roles should be handled a separate way in GroupHierarchyManager, because users (which don't have any membership) can have Anonymous user and Outsider roles, but they in the same time they don't have any records for membership, but GroupHierarchyManager build the mapping based on membership information.
I'm checking this case, I hope I will find a solution
Comment #241
lobsterr commentedI have migrated the permission handling to a new permission layer provided by group module. More information can be found here #3041087: Update the new permission layer to be alterable and #3041094: Group permissions can now be altered.
We don't need an event to handle permissions. I have removed the code related the events. Also there is a new permission calculator InheritGroupPermissionCalculator, which handles subgroup permissions.
Comment #242
jedgar1mx commented#236 works for me now. I'm running PHP 7.2 and Drupal 8.7.4
Comment #243
socialnicheguru commentedpatch 241 produces this error
because of this line which is introduced in the patch:
ggroup.services.yml:7: class: Drupal\ggroup\EventSubscriber\GroupEventSubscriberWhere is the GroupEventSubscriber?
Comment #244
lobsterr commentedMissed it
Comment #245
socialnicheguru commentedEDIT:
This is not in the rc2 version of group:
group_permission.calculator is not there
I am confused about which patch will work with the group r2.
When I apply the patch from https://www.drupal.org/project/group/issues/2736233#comment-13104478
I get this error:
delete previous comment.
Comment #246
walli commentedHello @LOBsTerr,
Thank you for this useful patch :)
When i apply the patch port-subgroups-2736233-244.patch, and i run drush updb, the hook updates can't be detected, so im always having this error :
The website encountered an unexpected error. Please try again later.</br></br><em class="placeholder">Symfony\Component\DependencyInjection\Exception\ServiceNotFoundException</em>: You have requested a non-existent service "cache_context.group_membership.roles.permissions". Did you mean one of these: "cache_context.group_membership.audience", "cache_context.group_membership.roles"? in <em class="placeholder">Drupal\Component\DependencyInjection\Container->get()</em> (line <em class="placeholder">153</em> of <em class="placeholder">core/lib/Drupal/Component/DependencyInjection/Container.php</em>).i had to apply the hook update in a custom module to avoid the error. Would you help me or maybe im missing something ? Thank youComment #247
lobsterr commented@walli I have tried to reproduce your case, but unfortunately without success. If you can provide more information about your instance or even specific steps. I will check.
I have tried with a fresh instance + rc4 and dev version of the module.
Comment #248
lobsterr commentedI want to open a discussion with all users of this patch, because I want to improve the subgroup permission system.
I have recently spent a lot of time trying to find all user cases and how to make it work with a new permission layer, but currently I need your opinion.
1. Why do we need propagate permissions from subgroup to parent group. Does anybody actually use these settings? It is really confusing and I think we should remove it. (it is second part in the mapping of subgroups)
2. Currently, we can map any parent group roles to any subgroup roles, but in fact the anonymous, outsider and advanced outsider roles are not taken into account, because we get groups from memberships. My question is do we want to map roles only if a user is a member for both parent and subgroup? In this case anonymous, outsider and advanced outsider roles are ignored as it is right now.
3. Should we simplify these settings and just allow or not allow to propagate permissions from parent group to sub groups and get rid off mapping ?
4. Please provide some other examples from your projects
Comment #249
jedgar1mx commentedHey @Lobsterr, I don't think there is any need to propagate the permissions from child to parent. The bi-directional permissions will only complicate things and could be easily achieved by giving users multiple memberships. But that is just my take.
Comment #250
lukedekker commentedAs I mentioned, I haven't been following this issue quite as closely in the last few months. Skimming through things, I don't see any confirmed issues that are needing a resolution. I think it would be beneficial to have a solid roadmap of confirmed issues (and steps to reproduce if possible) that we can start punching through. I believe that is our fastest route to getting this stable and committed.
Comment #251
Quicksaver commentedResponse to #248
TL;DR I see a definite and useful place for bubbling permissions in subgroups. All of it can be implemented by custom logic per-project though, perhaps even simplifying its implementation depending on each project's individual needs (not our case). This is mostly a report of our specific use-case, I don't have a concrete opinion on whether bubbling permissions should be implemented by subgroups itself, or how comprehensive they should be.
---
In basic terms, in our system an organization (the parent group, call it overseer) works with several other organizations (its subgroups, call them delegates). The delegates contain a stock of products, and a set of actions to be performed on/with that stock, as well as own user management.
1. Each delegate cannot access the stock or members of other delegates, nor act on them. In our case, we absolutely want members of the overseer to also access and perform those actions on its delegates, without members of the delegates to act on the overseer (which also has its own actions, etc). The most direct, and I would venture logical, way to do this is create a set of permissions on the delegate (subgroup) and have it propagate to the overseer (parent group)'s members.
I'll admit your point about them being confusing, it took me a little bit to get my head around it when I first started configuring the subgroups. However, solutions around it for our system without bubbling permissions are undoubtedly more difficult. In fact, we had to implement a custom permissions handler because of a single peculiarity in our system, and ended up just using it also for this permissions bubbling (only because it was more freeing). But as @lukedekker mentioned, I can see a definite place for bubbling permissions in subgroups.
2. To me this is more of a strategy/organization point rather than a technical one. (None of anonymous, outsider and advanced outsider roles are relevant or used in our system, so I will not give an opinion on those directly.)
In our case, users can only belong to a single group, they cannot belong to both the parent and subgroup. Both overseers and delegates are independent companies that manage their own staff, it's much simpler for the editorial/administrative staff to visualize them in the system in that way as well, avoiding situations like "Why is this person listed in my company? I don't even know them."
Again, it's not a technical point, this is of course easily overcome by a custom permissions handler (like the one I mentioned in 1. does a bit already actually), or with a set of views and hooks to automatically add, show, hide and remove certain members from certain groups. I just don't think multiple memberships can, or should, always be the solution.
3. Hmm, tough question. In our particular case, this would not matter much. Right now the overseer basically has admin rights (all permissions) over the delegates. I can still see a case for mapping though, such as a division of the overseer's staff with a certain role being able to perform only stock-related actions on the delegates, but not user membership ones.
Comment #252
lobsterr commentedFirst of all, I want to thank everyone for your feedback.
To sum up
1) This option is not used, but we will keep it for some exceptional cases. It can be remove easily at any moment.
2) Users use mapping of member roles and it is the main feature here.
The only feature is missing from the current implementation is propagation of the rights from anonymous and outsider roles. I did it (check information bellow)
3) Users use this functionality as it is. So, we will not simplify it. We will give the users opportunity to map any role to any role.
4) No, new features are required at this moment.
Information about the current changes
1) Fixed the bug with cache, when we build group inheritance structure
2) Improved the cache for "InheritGroupPermissionCalculator". I added Group Content Type as a dependency. It means every time we save a new role mapping configuration the permissions will recalculated
3) The main improvement, we can propagate and bubble up anonymous, outsider and advanced outsider roles to member roles.
Comment #253
lobsterr commentedI have noticed that I choose the wrong context it should be SCOPE_GROUP_TYPE context for InheritGroupPermissionCalculator
Comment #254
remotebox commentedI have just tried patch #253 and am getting the following error when trying to view subgroups:
Symfony\Component\DependencyInjection\Exception\ServiceNotFoundException: You have requested a non-existent service "cache_context.group_membership.roles.permissions". Did you mean one of these: "cache_context.group_membership.audience", "cache_context.group_membership.roles"? in Drupal\Component\DependencyInjection\Container->get() (line 155 of /var/www/html/web/core/lib/Drupal/Component/DependencyInjection/Container.php).I am using PHP 7.2, Drupal 8.7.6 and Group 8.x-1.0-rc4.
Comment #255
adrianodias commentedwhile trying out the new patch I noticed that there was a regression on group.install and gnode.install, committed changes from 6eaa050e39de8369ff6ca9d070992ea8ead363e5 got removed.
here is a new version of the previous patch where the following was addressed:
- fix the regression,
- there was a problem when trying to apply the contextual filter "Has parent group ID (with depth)" (the default value of checkboxes must be a array)
Comment #256
lobsterr commented@remotebox, Do you use the latest version of the group ? This service was removed "Removed the unsafe group_membership.roles.permissions cache context instead of deprecating it." in https://git.drupalcode.org/project/group/commit/b542c0ce2f2186e7c8cea2ae.... It is nothing to do with the patch.
Comment #257
remotebox commented@LOBsTerr, Sorry you are right - I was only using the latest stable release. I updated to the dev release which fixed the issue - thank you.
Comment #258
kkasson commentedI'm having some trouble getting this to work. I've created a fresh test installation to eliminate extra variables, and I just can't get this module to do anything. I can't tell if the module isn't working or if I'm doing something wrong. I assume the problem is on my end since it seems to work for everyone else, but I can't at all figure out what I'm missing.
Here's the situation on my test site. This will be a little verbose but I want to describe as exactly as possible to narrow down the problem.
I have a group type called Parent Group with a single group belonging to it called Parent. There's another group type called Child Group with a single group belonging to it called Child. Parent Group has roles of Parent 1 and Parent 2, and Child Group has roles called Child 1 and Child 2.
I'd like for members of Parent Group having the Parent 1 role to have access to the Child Group (and have the role of Child 1).
I installed the subgroup plugin for Child Group on Parent Group and mapped Member to Member, Parent 1 to Child 1, and Parent 2 to Child 2. I set Member, Child 1, and Child 2 to have view access to Child Group. I added Child as group content to Parent, and created a user called testuser.
I added testuser as a member of Parent, and gave him the role of Parent 1. testuser does not have a membership on the Child Group. testuser is unable to view Child. I then tried removing view access for Members and adding testuser as a group member on the Child Group. My hope here was that he would inherit the Child 1 role (since he has Parent 1, which is mapped to Child 1), and therefore have view access. He is still unable to view the group. I also tried reversing everything and mapping the child roles to the parent roles. I gave testuser the role of Child 1, and took away the role of Parent 1. testuser is then able to view the child group, but unable to view the parent group.
Is there some step I'm missing to get it to work? I've tried to debug the code and find what's happening but I'm not sure how's it supposed to work to know what I'm looking for. I did find a couple things that might be relevant:
GroupHierarchyManager->getInheritedGroupRoleIdsByUser loops through the group memberships that belong to the user. It appears that this completely prevents my first case from working, when the user has a membership to the Parent group but does not have a membership on the child group. Is that correct?
When I added the membership to the child group, it did appear that the above method returns the mapped Child 1 role correctly. However this doesn't seem to have any effect, as the user is still not able to view the group even though the Child 1 role has view permission.
Comment #259
lobsterr commented@kkasson, Thank you for your detailed report. I found the issue, I will present a new patch soon
Comment #260
lobsterr commentedSo, far I have found the next issues and we need to address them
1) When we map the roles parent -> subgroup, the user receive the roles of subgroup, but should get parent's roles. The same problem when we use bubbling of the roles from subgroup -> parent
2) When we do the mapping, we don't check that user actually has these roles in parent or subgroup.
3) When we have more then two levels the mapping of the roles is incorrect.
Parent group (type 1)
-> Child group (type 2)
---> Child child group (type 2)
"Child child group" and "Parent group" gets roles mapping from "Child group" and "Child child group"
Comment #261
lobsterr commentedI have fixed two first points. The third point a too complicated. I need more time.
Please, test it and report back
Comment #262
jayelless commentedHey Guys. Just a heads up here.
While I really appreciate all the effort that is going into getting sub-groups and this patch working correctly, I think that it is now getting overly complex, which I believe is preventing progress in having the patch ready to be committed.
My use cases require only stable sub-groups without any aspect of role inheritance, so can I suggest that the effort is split, so that the the basic sub-group functionality is in the ggroup module, with all the complex role inheritance moved into a separate sub-module or even an new contrib module. I think that the porting of sub-groups could then be completed and accepted more quickly, while the complex use cases for role inheritance are discussed separately.
Is there any support for this approach?
Comment #263
kkasson commented@LOBsTerr, thanks for the updated patch! It helped but I found some more issues.
1) The conditions in getInheritedGroupRoleIdsByMembership never apply to my configuration. I have a group A and a child group B. Member of A is mapped to member of B. My test user is a member of A and not of B. The role should inherit from parent A to child B and the test user should be a member of B.
$role_map correctly returns that mapping. However, since the method loops through group memberships, $group_id and $membership_gid both point to group A. Therefore $role_map[$group_id][$membership_gid] is always empty.
I made some changes and got this working in my case - I'll post the code below. I don't want to add it as a new patch because I don't know if it actually works, but hopefully someone here might be able to look at it and make any needed changes. It seems that the group graph is being used to generate the role map, but we also need to loop over the graph to find the inherited groups, since the user doesn't necessarily have group memberships in the other groups. The getGroupSubgroups/getGroupSupergroups methods weren't being used at all before. I've only tested this with a single group of each type, so I don't know if my changes might cause problems in other cases.
2) The graph doesn't seem to always work, or at least there are cases that it isn't designed to handle. It seems to correctly trace the path from parents to children, or children to parents, but it breaks when there are both types of inheritance at once. Here's my test case for this. Each letter is a different group type, and I have one group of each group type:
Group A has a child Group B. Group B has a child Group C. Group C has a child Group D. Another group type, Group L, also has Group D as a child.
A member (parent) is mapped to B member (child). B member (parent) is mapped to C member (child). C member (parent) is mapped to D member (child).
D member (child) is mapped to L member (parent), using the subgroup to parent group mapping.
Group B correctly picks up the role from A, and C picks up A through B. D also picks up A, through C and through B. The test user is a member of A, and therefore inherits the member role in B, C, and D. He's correctly able to view D.
Since he is now a member of D (through the inheritance), his role should inherit from the child group D to the parent group L, from the subgroup to parent group mapping. However this doesn't get picked up in the graph, and there's no path in the graph from L to C, B, or A. I tried to quickly add some SQL to add the rest of these path, but I couldn't get it to work without adding thousands of extra paths from looping back and forth over each other. I don't know if it's even supposed to have these paths, but they're needed with the way I'm inheriting the group permissions below.
3) The caches don't seem to always be working for me. I added a hook on group_content_update to rebuild the role inheritance, in addition to the insert and delete hooks. If you update the role mapping from a parent group to a subgroup, it wasn't updating the cached role inheritance. Even with that I was still getting the wrong inheritance cached sometimes. There's probably still somewhere else that things need to be invalidated, but I haven't narrowed down when exactly it's happening.
Here is the code I changed for 1). This seems to work for most cases, except those described in 2).
In GroupHierarchyManager.php, change the end of getInheritedGroupRoleIdsByMembership to the following:
In InheritGroupPermissionCalculator.php, change the end of calculateMemberPermissions to the following:
Comment #264
kkasson commentedA couple more notes to the above:
1) This line in GroupHierarchyManager.php is definitely broken with my other changes. This could perhaps be the source of my caching problems.
2) I was also noticing some major performance problems coming from calculateAuthenticatedPermissions in the main Group module's ChainGroupPermissionCalculator. It was calling the merge function thousands of times. I added some quick static caching that solved the problem for me, at least as a workaround. The other methods in that file were being cached correctly, but it was still having to merge those cached results. I'm not sure if that's actually an issue with that method itself or if it indicates a problem further down the line in these subgroup permissions.
Comment #265
lobsterr commented@jlscott I like the idea, I think we should do it. I started to work on it.
1) I propose to create a separate ticket for subgroup code only;
2) This issue we will keep for a new module. I propose the name ggroup_role_mapper, because this ticket keeps the most of the discussions related to the group role mapping
@kkasson I will investigate the cases provide by you after the split of the modules.
Comment #266
lobsterr commentedFinally, I have done the split. I decided to create two separate tickets. So, it would much easier to handle it and for newcomers easier to contribute. In this issue there are too many comments.
1) Subgroups core module #3084140: Subgroups core module
2) Subgroups role mapper module #3084153: Subgroup role mapper
Comment #267
catchLet's mark this as duplicate of the two issue in #266 and continue in those.
Comment #268
catchEr except the patch didn't make it to #3084140: Subgroups core module.
Comment #269
catchBoth patches are uploaded to the spin-off issues, marking as duplicate now.
Comment #270
andrewsizz commentedDelete view subgroup, as this view have references to field gc__group which already not exists
Comment #271
andrewsizz commentedupdated patch for latest version
Comment #272
dbielke1986 commented@AndrewsizZ
Why did you post something in an closed item.
This issue have been splitted up to two seperate items:
#3084153: Subgroup role mapper,
#3084140: Subgroups core module
I think we should not update this issue right here...