

 The 2026 Drupal Business Survey is open. Your response will help shape the future of the Drupal business ecosystem.
Problem/Motivation
Follow-up to #2503755: Switch from user login block to login menu link and search block in standard profile
login link has no destination=[current.path], so dumps you on the profile
Proposed resolution
Add destination.
User interface changes
None.
API changes
None. API addition: links can set the data-current-path-destination attribute to automatically get the destination query argument
Data model changes
None.
Why this is an RC target
This is severe UX regression introduced by #2503755: Switch from user login block to login menu link and search block in standard profile
| Comment | File | Size | Author |
|---|---|---|---|
| #159 | core-login-destination-2582797-159.patch | 26.62 KB | vdsh |
| #155 | interdiff_153.txt | 4.77 KB | jastraat |
| #155 | core-login-destination_2582797_155.patch | 25.64 KB | jastraat |
| #153 | core-login-destination-2582797-153.patch | 25.6 KB | benjifisher |
| #153 | interdiff-2582797-149-152.txt | 814 bytes | benjifisher |




Comments
Comment #2
effulgentsia commentedLoginLogoutMenuLink is a class in user module, so setting that as the Component for this issue. Unless someone believes the right fix is somewhere else, in which case set the Component to that.
Comment #3
webchickYeah, we should definitely fix this. I would call it major, since it's a regression.
Funnily enough, I did not catch this in manual testing since the default front page is so sparse. :P (one of the UMN 2015 issues.) In a quick glance it didn't look much different than the similarly sparse user/1 page. :(
Comment #4
moshe weitzman commentedDo folks agree that the destination querystring param should be added via JS in order preserve our current two cache contexts (anon or authenticated)? How can I add an id on this link so that js can find and append a querystring?
Comment #5
catchIf possible we should placeholder it in PHP, currently have no js for anon users and that's worth retaining.
Comment #6
wim leersWe should use the same approach as for "active" links (adding
.is-activeto active links): JS-based solution for auth, PHP-based solution for anon.(The assumption being: pages for anon users are cached in the Page Cache (or a reverse proxy) anyway. So it's fine to do the work in PHP for anon users. Of course, this should be overridable, in the same way that it is overridable for authenticated users.)
I'll take this on
Comment #7
wim leersThis fully implements that, the only thing missing is test coverage. (Which can be inspired by
ActiveLinkResponseFilterTest).This introduces:
data-current-path-destinationattribute, which is used as a signal to give the link that it lives on adestinationquery argumentcore/drupal.current-path-destination-link(much likecore/drupal.active-link): a small bit of JS to add thedestinationquery argumentCurrentPathDestinationLinkResponseFilter(much likeActiveLinkResponseFilter)system_page_attachments(), to add the JS library for authenticated users, just like it does for active linkscontextual.js: it now reuses the logic of that JS libraryComment #8
wim leersComment #9
catchIs it OK to do that for the logout link? It could end up with 403s that way.
Comment #12
moshe weitzman commentedGood point about logout.
The approach looks sound to me. I searched for "'destination' => " and just found a couple comment links which are candidates for this treatment. We currently placeholder those so no rush to convert those.
Comment #13
wim leers#9: good point. Now only doing it for the "Log in" link. Zero behavior change then.
Comment #14
wim leers#12:
Indeed, there are more places that could benefit from this, but let's start small :)
destinationquery argument. Because otherwise, we'd have to re-render it for every page. Because it is omitted, it's possible to cache it on the client side.Comment #17
wim leersFixed the test failures. All contextual link test coverage that needs minor updates.
The
UserPasswordResetTestis still failing, there's some kind of endless loop problem there that I still have to figure out :)Next: adding test coverage. The JS will need manual testing, of course. (And preferably the +1 of @nod_ or @droplet.)
Comment #19
wim leersLast fails fixed, test coverage added.
Comment #20
berdirI'm not sure I understand why we need the JS based solution at all?
Also the logic of that check (add js for auth users only) seems flawed. We don't add JS for anonymous users *by default*. Almost any non-trivial site out there will however do exactly that. If anything, then it would have to be a check for whether we are adding JS or not?
Shouldn't a response filter work for anything, e.g. also an ajax response that adds a link with a destination?
Comment #21
wim leersWe use the same logic for "active" links and that has worked out well.
Any site that serves JS to anon can easily override this behavior.
To answer the generic question: How could it possibly work for "anything". It can only work for specific types of responses.
To answer the specific question: If an AJAX response is involved, then JS is involved, and it's implemented as a behavior, so all new HTML added via AJAX responses will also get the destination query string.
Comment #22
fabianx commentedThis feels a little excessive to me, too.
Can't we just use the normal placeholder pattern for the current URL we use elsewhere as the minimum solution?
Having one unified placeholder for the current url has several advantages even for ESI - especially with Varnish 4.1.
---
Even if we decide to use a JS based solution for placeholdering current url links, should we then not just use a placeholder strategy to do so to unify?
e.g. replace the [current url] placeholder with #attached library or in case of anonymous replace with the current url directly.
Comment #23
moshe weitzman commentedFWIW, we have an identical need at #2579907: Re-introduce the destination parameter in the Devel menu items. If the login link were the only one, I think standard placeholder would be fine. But I think this is a more common need than one might think. We could end up with a dozen such placeholders.
Comment #24
wim leersWhere else do we use this?
I'm assuming you mean
Rendererplaceholders here (i.e.#create_placeholderand#attached[placeholders]).Hrm… so basically use the same approach as
\Drupal\Core\Access\RouteProcessorCsrf::processOutbound(). That could work too. Except… how are you going to add those placeholders?We have a
#attached[placeholders-based solution for CSRF tokens because the route declares it needs a CSRF token, and we have outbound route processors, therefore we can do this.But the
destinationquery string can appear on any URL. Neither outbound route processors not outbound path processors help with that.But even then we still have a use case for the JS: contextual links. Contextual links already use this pattern. It makes absolutely no sense to use
#attached[placeholders]there, because the contextual links are cached across page loads, on the client-side. The only thing they are lacking, is the "destination" query string.For that, we'll always need a JS solution.
So, I think to arrive at the best solution possible, we need to thoroughly analyze the pros and cons of the two possible solutions.
Comment #25
fabianx commentedWe could perhaps add a default placeholder via system_page_attachments_alter().
I think all placeholder processing logic already checks if a placeholder exists at least once on the page, so adding it unconditionally should not hurt?
Just would need a generator or something like this.
Yes, we need the JS and class anyway, but the question is can we make the processing in the response subscriber simpler.
Comment #26
wim leersIf you want to use the Render system's "placeholder" subsystem, then you need to ensure there's a unique string to be found somewhere in the response. i.e. discovery mechanism is string parsing.
Whereas a JS solution cannot use string parsing. It must rely on the DOM.
That's why the server-side part of the JS solution looks like it does: it mimics the JS logic. The reason it is relatively complex: because PHP's
DOMDocumentsucks/is very slow, and therefore implementing this tiny subset of logic of DOM parsing to find the right place in the DOM makes it much faster. See #1979468-238: ".active" from linkGenerator(), l() and theme_links() forces an upper limit of per-page caching for all content containing links.Comment #27
effulgentsia commentedI think #25 is worth exploring.
Can we do that with a system similar to CacheContext services, but a little different, e.g., CachePlaceholder. But the idea is that via services.yml, you can make an association between an identifier (e.g., 'path.current') and an object that can return a value for that. Then could a CachePlaceholdersManager generate unique placeholders based on the identifier, such as:
Then LoginLogoutMenuLink::getOptions() could do:
And then at placeholder replacement time (whether that's a function added in system_page_attachments_alter() per #25 or something else) we iterate all CachePlaceholder IDs and replace all occurrences of the corresponding placeholder string with the service's getValue() method.
Or if there's a way to optimize it so that prior to writing to dynamic_page_cache we do the iteration and store the IDs that were found so that on a dynamic_page_cache hit we only need to iterate the ones used by that page, even better.
Comment #28
fabianx commented#27: Yes, that is exactly what I thought. A CachePlaceholder manager like thing.
It would be great to have that anyway and it would also be great to easily register 'global lazybuilders' so to speak.
As get-me-the-current-url is very very useful.
e.g. lets take a [current-url] token in a block, which makes the block cacheable only per url, but with the transparent service it gets very simple to use a placeholder in between and just at rendering time replace it.
Comment #29
wim leers#27 + #28: But we don't want to do all that server-side stuff for dynamically generated responses (i.e. for auth users). So we need a JS solution for that. So, let me repeat #26:
I.e. how does that system allow the JS to still work?
I don't see the value in reinventing the wheel here and potentially coming up with new APIs during RC. We can reuse a pre-existing pattern, that has been working fine for almost two years now (it landed on January 23, 2014).
Finally, the JS-based solution is also a great fit for https://github.com/rails/turbolinks/, which we could (and should?!) add in addition to BigPipe, for maximum speed-up. It allows us to even start from a server-side rendered destination query string and replace it when we transition to a different page using Turbolinks. Without some marker on the link, we would not be able to find it.
Comment #30
effulgentsia commentedWhy? I think #27 would actually be quite fast to do server-side after a dynamic_page_cache hit for an auth user? Or am I wrong about that?
Comment #31
webchickRegardless of implementation, IMO it would be great to get this committed during RC, so adding the tag so core committers can discuss it.
Comment #32
wim leersYes, that is wrong IMO.
By the same reasoning, we should do this for "active" links too.
The JS solution allows us to do the work after the page has begun rendering in the browser — it allows us to do a computation basically in a JIT fashion.
The PHP solution requires us to do the work before sending the relevant HTML. In HEAD, that means literally blocking the response on those placeholders being processed. In a BigPipe world, that means that every placeholder that is rendered also needs to go through this "cache placeholder response filter".
Let's not forget it can't be implemented as a regular placeholder (
#attached[placeholders]), as I said in #24: So then you're back to a response filter-style approach (like this patch does).In general: if there's simple replacement work like this happening, that may affect many things on the page, and it's not something critical… then it's better to do it in JS, because it'll result in better perceived performance, because the server isn't slowed down by it.
Comment #33
effulgentsia commentedI'm not convinced that we do, but if we really want JS for auth and no-JS for anon, then can we do this:
LoginLogoutMenuLink::getOptions() does:
regardless of user.
system_page_attachments() stays the same as #19: adds the library only for authenticated.
We add an outbound path processor that only for anonymous does:
Comment #34
effulgentsia commentedThat was a xpost with #32, not a reply to it.
Comment #35
wim leers#33: yes, that's a way to still allow the JS to work, i.e. that would address my remark in #29:
… except that
$optionsas passed to\Drupal\Core\PathProcessor\OutboundPathProcessorInterface::processOutbound()apparently does not have either the final value or changes to it may be lost. IIRC @pwolanin ran into that a week or so ago.Can somebody explain to me why we are seemingly diverging so much, even though we can literally apply a solid, battle-hardened pattern that we've had for almost two years? It seems to me like all this should be follow-up material, we should fix the regression with as few changes (and thus as few new patterns) as possible.
Comment #36
effulgentsia commentedYeah, that's fair. Per #26, although #19's
CurrentPathDestinationLinkResponseFilterseems pretty ugly, it just copies the pattern used by HEAD's existingActiveLinkResponseFilter, which has been in HEAD in more or less its current form for 6 months, and the ugly part existed in HEAD in SystemController for over a year before that. Based on that, I guess it does make sense to apply the same pattern here and punt ideas for improvement to follow-ups.Comment #37
wim leersFor the part, pinging @nod_ and @droplet.
Comment #38
wim leersThis has now been silent for 25 days. This is a huge usability regression and will impact many, many end users of Drupal.
IMO we totally should get this done before release.
Comment #39
Bojhan commentedDoes this need some committer direction to move forward? I am also a bit worried, we might launch with this and over a implementation discussion that can easily be refined after release.
Comment #40
fabianx commentedUhm, we are waiting for manual testing from nod_ and/or droplet as far as I can see.
I stated in IRC that I am fine with copying the same pattern for now.
Assigning to nod_ for feedback.
Comment #41
timisoreana commentedLogin and logout work for
1) /contact
2) /node/1
3) homepage
4) /search (without "keys" parameter)
and
5) Logout for /user/1
6) Login from /user/register?destination=/node/1%23comment-form
but login don't work like expected for:
1) /search (with "keys" parameter)
1) Enter something on search field
2) Click Search (result page /search/node?keys=something)
3) Login
Actual result:/search/node (missing keys parameter)
Expected result:/search/node?keys=something
2) Pages with access denied
1) Go to /node/add
2) Login
Actual result:/system/403
Expected result:/node/add
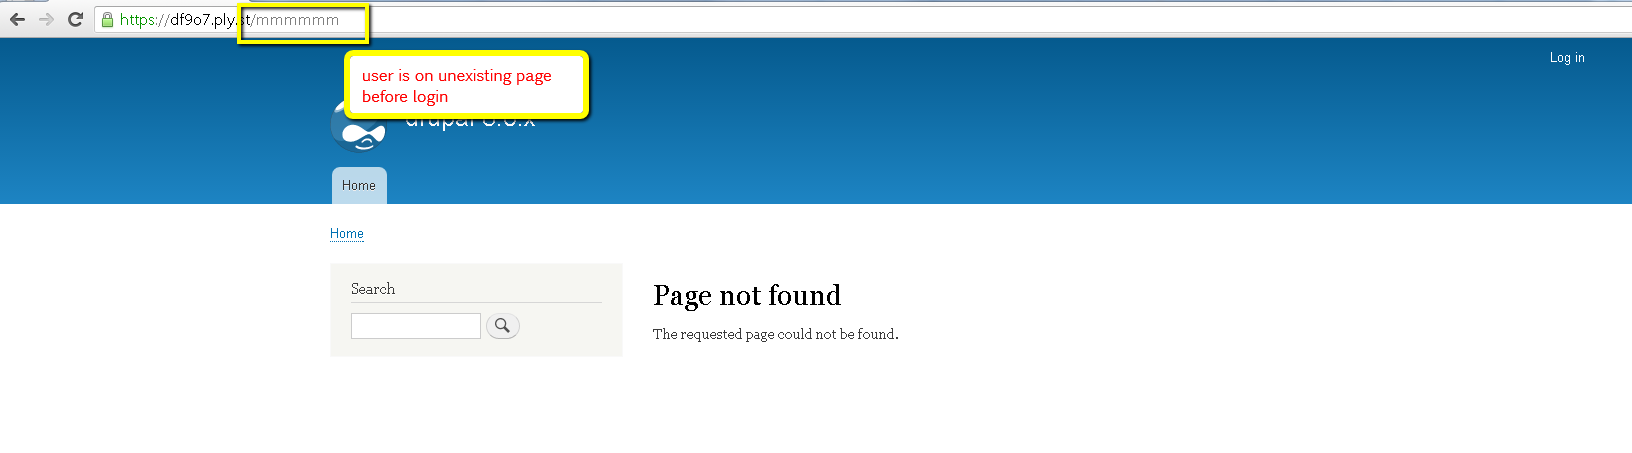
3) Unexisting page
1) Go to /mmmmmm (or other unexisting page)
2) Login
Actual result:/system/404
Expected result: homepage (or other accessible page for user)
Comment #42
wim leersFunny, nobody thought of the query string before you!
I'll fix that, but this still needs a JavaScript review, so setting back to "needs review" for that.
Comment #44
andypost403/404 should be fixed also
missing 2nd required argument (delay)
Comment #45
wim leersFirst, a straight rebase against HEAD (no conflicts encountered). Should be green again.
Comment #46
wim leers#41 + #44: regarding 403/404 getting the wrong responses: that is caused by this being 4xx responses being generated incorrectly in HEAD. If you apply this patch and #2595695: 4xx handling using subrequests: no longer able to vary by URL, you'll see that it does work correctly.
Comment #47
wim leersComment #48
wim leers#44: RE:
setTimeout(): good catch, that should have a delay of zero.Comment #49
andypost@Wim otoh there could be implementation based on
HTTP[referer]header that most browsers sendingComment #50
wim leersNow also fixed #41's query string problems.
#49: well, that's for a distant future, where HTTP/1 doesn't matter anymore. :)
Comment #51
alexpott@xjm and I agree that this is an RC target.
Comment #52
heykarthikwithuMinor change in the comment block
@param \Symfony\Component\HttpFoundation\RequestStackshould be replaced by
@param \Symfony\Component\HttpFoundation\RequestStack $request_stackComment #53
wim leers#52: Good nitpick, thanks. Can be fixed on commit.
Comment #54
nod_Removed the nested attachBehavior call and called directly the attach function, contextual depend on the script so we're sure it'll be there.
Apart from that the JS is ok with me.
Comment #55
wim leersAlright!
Who dares RTBC? :)
Comment #56
fabianx commentedRTBC - looks great to me!
Comment #57
effulgentsia commentedWe're in the final home stretch of preparing 8.0.0, and we won't be committing the majority of "rc target" issues any more, but still leaving the tag on them to triage them for patch-release or minor-release post 8.0.0 release. Meanwhile, switching to "8.0.0 target" for issues we'd still love to get in before 8.0.0.
Comment #58
yesct commentedNice. I see the test for the query added in #50
Might be good to have a patch and tests-only patch so reviewers can see the fails and make sure they are failing in the way we expect.
Comment #59
wim leersComment #60
alexpottThis does not work for me.
http://DOMAIN/user/login?destination=system/403I have render cache disabled.
Comment #62
wim leers#60: that is merely another known bug you are seeing, see #46.
Comment #64
alexpottI'm not sure what the point of the JS version is tbh - if a user is logged in they are not going to have a log in link. Also the current path in drupalSettings for
/adminis completely wrong - it is system/403 :(Comment #65
alexpottHere's a fix and test for anon.
Comment #66
alexpottSo I think that the currentPath being system/403 or system/404 in drupalSettings feels like a pretty serious bug.
Comment #68
wim leersOkay, let's answer this again, point-by-point:
#64:
AFAICT there are plenty of use cases where we want to have a
?destination=<current location>query string for authenticated users. In Drupal core, there's only contextual links. In contrib, there will surely be more. Anything where the authenticated user does something and should end up back in the place they started can use this.#64 + #65:
This is what you already said in #60, to which I already replied in #62.
Drupal 8 HEAD handles 403/404 responses incorrectly. This is a known bug. Apply #2595695: 4xx handling using subrequests: no longer able to vary by URL and it will work as expected. That patch has already been deemed okay to be committed in a patch release of Drupal 8.0.x.
#65's work-around is wrong; the proper fix is to fix how 403/404 responses are generated, which is what #2595695: 4xx handling using subrequests: no longer able to vary by URL already fixes. The patch there is ready.
I think it's fine if this gets committed during the 8.0.x cycle. It doesn't have to happen by 8.0.0. Even though it results in a frustrating UX. If we don't feel 100% about this patch, we shouldn't commit it now, a day before 8.0.0.
Comment #69
alexpottSo applying #2595695: 4xx handling using subrequests: no longer able to vary by URL doesn't fix the currentPath in drupalSettings when the a user is logged in but does not have permissions to access /admin...
I would argue the currentPath and currentPathIsAdmin are both wrong here.
Comment #70
alexpottAlso I removed the "8.0.0 target because I think we need to fix https://www.drupal.org/node/2595695 - therefore postponing and marking as a minor version target.
Comment #71
wim leers8.1.x has been opened by now. The patch in #65 still applies.
Keeping postponed because #2595695: 4xx handling using subrequests: no longer able to vary by URL needs to be fixed first.
Comment #72
wim leers#2595695: 4xx handling using subrequests: no longer able to vary by URL landed.
Comment #73
wim leersReuploading @alexpott's patch of #65, straight reroll.
Comment #75
wim leersStill the same 2 failures after ~7 weeks, good.
Comment #78
wim leersI can't believe not more people are complaining this is annoying?! I've done the work to fix it way back then, but it seems it's not actually a problem? It definitely annoys me though. But we went two minor releases without a single comment, which I think is grounds enough to demote from major to normal, and probably even to minor.
Comment #79
moshe weitzman commentedIt bugs me a lot.
Comment #80
tim.plunkettIt is very annoying.
Though I think if the installer didn't log you in directly, it would be even more widely reported.
I think 'normal' is a better compromise between major and minor.
Comment #81
wim leersPeople are now creating new contrib modules to fix this, and they're not finding this issue.
#2824418: [D8] Login Return Page
Comment #82
gnugetOk, straight reroll from #73.
Comment #83
gnugethahaha I forgot the patch. xD.
Comment #85
gnugetI fixed the more straightforward tests.
Let's see what the bot says.
Comment #87
Fidelix commentedComment #88
gnugetI think this is beyond me, I tried today to fix the failing tests and BigPipe always fails in my local (even without this patch) and the fail related with outside_in return:
I will leave it for now, in case someone else wants to give it a try.
Regards.
Comment #89
mlncn commentedThis issue was hard to find. I was fairly certain it was a regression and also expected lots of people to be complaining about it, and was specifically looking for this issue, and somehow didn't find it. Gnuget made a whole module to work around it.
Comment #90
cilefen commentedI think folks had settled on normal priority, so you'll need to make a case for raising it to major.
Comment #91
wim leersThe BigPipe fail is trivial: in HEAD, it doesn't expect the
core/drupal.current-path-destination-linklibrary to be listed, but this patch adds that. So BigPipe's expectation needs to be updated.The
StandardTestfail looks like it may have a small error in its expectation in the new test assertion.Comment #92
gnugetThanks for the feedback.
New patch.
Comment #96
quietcorn commentedIs there still no drupal 8 functionality that returns a user to the page they clicked the login button from? I've been searching for how to do it, came upon gnuget's blog post, then his unapproved module to here. This seems like something that drupal should be able to do right?
Comment #97
gnugetYes, this is a regression, this is something that Drupal 7 does correct and D8 doesn't.
The last patch just needs a bit of work and should be ready to be committed, due to my experience working with JS I wasn't able to figure it out the problem.
I hope to try again soon.
Comment #98
quietcorn commentedI'm glad you are working on it gnuget. I'll keep an eye on this thread with hope and anticipation.
Comment #101
olafkarsten commentedRerolled. Wasn't as straightforward as I hoped. Patch is somewhat smaller now. Some tests have changed over time, and so some code just becomes obsolet.
This seems to be the case for :
BigPipePlaceholderTestCases
MenuTest
UserLoginTest
DisplayTest
NodeRevisionsTest
Lets see what the bot says.
Comment #104
olafkarsten commentedNext round. Locally the ContextualDynamicContextTest runs just fine. Needs some more investigation. Hope this one fixes the StandardTest fail.
Comment #106
olafkarsten commentedDon't know for what the base_uri stuff in StandardTest is for. Removing it, fixes the fail - at least locally. So lets ask the boot again.
Comment #107
jonathanshawI don't think removing it is the right solution, it looks like it's testing something real. Can you figure out what href the assertion is expecting and what it's actually getting?
Comment #108
lolcode commentedI tested the patch in #106 and it did not play well with the cas module enabled
My use case: I have cas "forced login" turned on for all "/user/*" links on D8 client sites so that clicking on the login menu link actually redirects to /caslogin which in turn redirects to my SSO server then back to the client site.
Without the patch:
* I am redirected to my cas server for login and then dumped back to /user as this issue description notes
With the patch:
* I am redirected right back to my current page and never go to the cas server
Comment #110
azinck commentedHere's an attempt at a straight re-roll of 106 against 8.8.x -- not trying to fix any of the test issues mentioned in 107.
Comment #111
azinck commentedAnd here's one that applies cleanly to 8.6.x.
Comment #112
shaalI tested #110.
Using Drupal 8.7.x + Umami.
I checked it on a multilingual website. The login link works great on every page, it goes to the login screen and then redirects to the page I started from.
Comment #113
alexpott@azinck you might want to upload #110 again as it is the rtbc patch and you want the rtbc retest to pick that patch and not the 8.6.x one.
Comment #114
alexpott@shaal it sounds like #107 and #108 need to be addressed.
Comment #115
azinck commentedRe-uploading #110 to make the 8.8.x patch the current one.
Comment #116
alexpottAlso realised that #107/ #108 are yet to addressed.
Comment #117
azinck commentedFWIW I'm pretty sure #108 is a bug in the CAS module and how it's handling its redirects.
Comment #118
alexpott@azinck that might be the case but then that means we need to somehow either fix that module - it's quite widely used - or at least prep a workaround so sites can rely on the old behaviour.
Comment #119
GrandmaGlassesRopeManBefore I take a bigger look, lets move the changes to the correct place. Thanks.
This should be in an .es6 file and then built.
These changes should be in the .es6 file and then run the build process.
Comment #120
bkosborneRegarding #108 - I am the maintainer of the CAS module. This patch just surfaces a problem in the CAS module. It's not a problem with this patch. I'll fix the issue in #3029612: CAS automatic login should respect existing destination parameter
Comment #121
lolcode commentedI can confirm that the issues with CAS are resolved.
We are seeing that the patch in #110 works on all pages except the front page. On the front page the destination parameter is still unset.
Comment #122
jonathanshawSo we are NW for #107
Comment #123
moshe weitzman commentedSo close, yet so far.
Comment #125
vdsh commentedI tested the patch, it seems to be working fine to add destination to login link. 2 comments though:
- If I am on the homepage, I got "destination=" added - which then brings me to the user profile page after login (not back to homepage)
- If I am navgating from login page to register or lost password & back to login page, I am losing my destination parameter. It would be great if the destination is saved until I log-in or cancel my registration / login process. What do you think?
Comment #126
azinck commentedI've just run into a bug caused by this patch. I'm trying to serve up HTML files as private files in Drupal and this patch attempts to call setContent on that response, which is not permitted since it's a BinaryFileResponse object so an exception is thrown:
"The content cannot be set on a BinaryFileResponse instance"
I'm honestly not sure of the best approach here...should we just check whether our response is an instance of the class or has the class as one of its parents? That would block anything that might extend that class but I suppose it's possible that some subclass of BinaryFileResponse *might* be able to handle a setContent call. Is there any other info we can key on to determine if calling setContent would be appropriate here? Or should we just catch the exception?
Comment #127
azinck commentedLet's try this. This includes a small reroll change for 8.9x plus adds a check to ensure we don't try to modify BinaryFileResponse responses.
Leaving as "needs work" due to the other issues flagged in this thread.
Comment #128
jonathanshawRe #126 can we catch the LogicException that BinaryFileResponse throws?
Comment #130
vdsh commentedRe-roll of #127 for 8.9 (only some small changes in the tests)
Comment #131
nod_Just tiggering the testbot see where we're at.
Comment #132
hardik_patel_12 commentedLast patch failed to apply , re-rolling patch , kindly review.
Comment #134
bob.hinrichs commentedPatch does not seem to apply to 9.1.3, for me, sorry.
I'll just add my voice to the outcry, that this has been broken for >5 years now, is unbelievable to me. Plus this issue node is more obscure than it ought to be, took me a while to come across it.
Thanks all for your work on fixing it.
patching file misc/current-path-destination-link.js
patching file modules/block/tests/src/Functional/Views/DisplayBlockTest.php
patching file modules/contextual/contextual.libraries.yml
patching file modules/contextual/js/contextual.js
patching file modules/contextual/src/Element/ContextualLinks.php
patching file modules/contextual/tests/src/Functional/ContextualDynamicContextTest.php
patching file modules/system/system.module
patching file modules/system/tests/src/Functional/Menu/MenuAccessTest.php
Hunk #1 FAILED at 61.
1 out of 1 hunk FAILED -- saving rejects to file modules/system/tests/src/Functional/Menu/MenuAccessTest.php.rej
patching file modules/user/src/Plugin/Menu/LoginLogoutMenuLink.php
patching file profiles/standard/tests/src/Functional/StandardTest.php
Hunk #1 succeeded at 268 (offset 1 line).
patching file tests/Drupal/Tests/Core/EventSubscriber/CurrentPathDestinationLinkResponseFilterTest.php
Could not apply patch! Skipping. The error was: Cannot apply patch https://www.drupal.org/files/issues/2020-08-31/2582797-132_1.patch
Comment #135
alexpottTher should be a .es6 version of this that we transpile to js.
I think we can use
encodeURIComponent()here instead and then we don't need to depend on jQuery - which is good because that is slowly being removed from Drupal.Comment #136
anmolgoyal74 commentedRe-rolled for 9.2.x. And addressed pointer in #135.
Comment #138
adityasingh commentedWorked on test case. Kindly review the patch.
Comment #139
capysara commentedWas #107 ever addressed? I don't see any follow up for it in the comments.
I manually tested on simplytest.me
On simplytest.me
Comment #141
vdsh commentedRe-rolled for 9.2.5 (a test got slightly changed)
Comment #142
vdsh commentedRe-rolled for 9.2.6
Comment #144
vdsh commentedRe-rolled for 9.3.0
Comment #145
jonathanshawI think that #107, #119 and #135 are addressed.
But we are NW for a decision on #128 and for test coverage of the issue raised in #126.
Comment #146
run fast think slow -lets4- commentedThis is my first reroll of this coding issue from #144 above.
Also fixed a white space coding issue from testbot.
Comment #149
hungdo commented#146 doesn't work with Drupal core 9.4, re-rolling a new patch file.
Comment #150
hungdo commentedComment #151
benjifisherI compared the patches in #146 and #149, and the re-roll looks good to me.
There are a lot of test failures, but I think they are all because of deprecated code. (I did not check them all.) For example:
That should be easy to fix. But see the change record: it might be more than a 1-line change. If you can run one of the failing tests locally, it will be a good idea to check before asking the testbot to try again.
Comment #152
hungdo commentedReplace the getMasterRequest deprecated function with getMainRequest, uploading a new patch file.
Comment #153
benjifisherMuch better! Only 1 test failure, not 1,305.
I think that remaining failure is real, although I get something different from the testbot. In fact, the testbot's report is confusing:
I get something that makes more sense:
That looks related to this issue, and I think this is a case where we need to update the test.
When I run the test with PHP 8.1, I also get this:
I think that should be fixed, too. It comes from these lines:
The patches in #149 and #152 are oddly formed: to show an empty line of context (neither added nor removed) they use an empty line. Every patch I have ever looked at until now uses a line with a single space. To my surprise, both
git applyandpatch -p1applied the patches without complaining. But theinterdiffutility failed.I am attaching
Comment #154
jonathanshaw@benjifisher do you have an opinion on #126 / #128 ?
Comment #155
jastraat commentedRerolling patch in #153 to address PHP 8.1 issue with stripos() along with deprecation of FilterResponseEvent. Does not address the test issue. Both @benjifisher's and this patch address the BinaryFileResponse issue as suggested in the #127 patch.
I'm including an interdiff which has some changes due to rolling the newer patch against the latest 9.4.x + the changes above.
Comment #157
jonathanshaw#153 suggests the remaining fail needs to be fixed by updating the test (the expectation I assume).
Comment #159
vdsh commentedRe-rolled #155 for 9.5.9 (not fixing the test issue)