

Closed (fixed)
Project:
Drupal core
Version:
8.0.x-dev
Component:
user.module
Priority:
Normal
Category:
Task
Assigned:
Unassigned
Issue tags:
Reporter:
Created:
20 Jan 2014 at 23:24 UTC
Updated:
29 Sep 2015 at 10:04 UTC
Jump to comment: Most recent, Most recent file

Comments
Comment #1
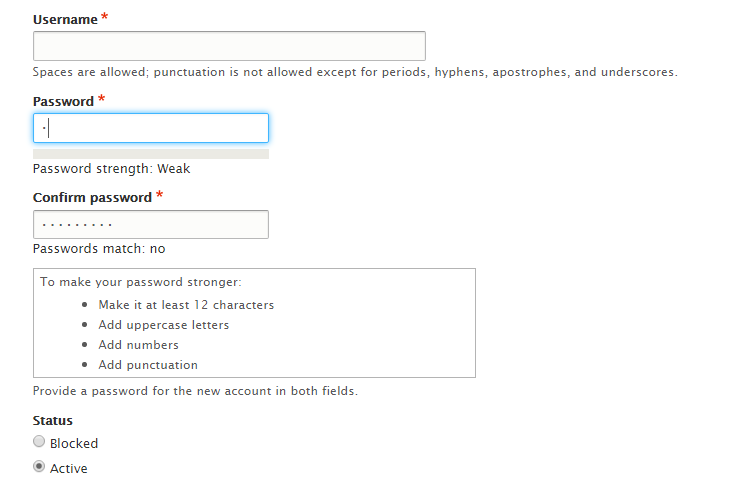
jbrauer commentedPatch to recommend that users use at least 12 characters which seems in most reading to be the low-end recommendation at this time.
Comment #2
jbrauer commentedComment #3
catchThis seems reasonable.
Also the numbers/mixed-case/punctuation we should make sure those disappear if the password is above a certain length as well. Obligatory link to xkcd.
Comment #4
alansaviolobo commentedreroll
Comment #6
alansaviolobo commentedended up exporting a reversed patch.
Comment #9
jbrauer commentedCode comment also needs update.
Comment #10
jbrauer commentedUpdate comment in patch as well.
Comment #11
gregglesThis seems like a decent improvement.
I'll say that folks "serious" about the idea of an accurate password strength indicator would be well served to use https://www.drupal.org/project/password_strength
Comment #12
gregglesOne more thought - the need for longer passwords, and how long is long enough is a site-specific question and it obviously changes over time. Rather than having this hard-coded, why not make it a variable? I don't think there needs to be an admin ui for it, but it could be in $conf in settings.php (or whatever the d8 equivalent is).
Comment #13
jbrauer commentedVery much agree with greggles in #12 ... this really should be a variable. I've not done that here in the hopes that a minimal patch had a better chance of getting in but if there's support for it think we really should have it as a variable.
Comment #16
anavarreComment #17
anavarreComment #18
anavarreStraight reroll. Doesn't address #12.
Comment #19
anavarreComment #22
anavarreComment #23
am_sreenivasan commentedWhat worked:
1. Patch applied succesfully without errors.
2. Patch code seems legible and clean to good standard
3. Solution worked and solved to reflect postive results during password creation in the last screen of Drupal installation
It certainly checks and mandates a longer passwrod with minimum 12, checked for a mandatory combination of upper case, lowercase, numbers and punctuations
4. Solution also worked and solved to reflect postive results during change password screen for admin
It certainly checks and mandates a longer passwrod with minimum 12, checked for a mandatory combination of upper case, lowercase, numbers and punctuations
5. Solution also worked and solved to reflect postive results during password creation and also change password screen for new users
It certainly checks and mandates a longer passwrod with minimum 12, checked for a mandatory combination of upper case, lowercase, numbers and punctuations
Suggestion: The hint text given for password mismatch is currently as follows
Passwords match: yes
Passwords match: no
To keep this connsistent with the hint text given under first password field "Password strength: Weak", the "Yes" or "No" should start with capital letters. So to make it read as follows
Passwords match: Yes
Passwords match: No
Comment #24
greggles@am_Sreenivasan - thanks for the review. I'd suggest making that upper/lower case problem a new issue. We should not sneak string changes into this issue as it could confuse translators.
ETA: not since the sentence was the opposite of what I meant.
Comment #25
anavarreFiled #2568023: Don't hard code maximum password length to address #12
Comment #26
alexpottThis seems a sensible security improvement to make. Changing a minimum value is not a feature request. Committed 767077f and pushed to 8.0.x. Thanks!