Problem/Motivation
A frontend reads an unsaved preview with the editor's session cookie. That only works when Drupal and the frontend share a site, or a proxy puts them on one origin. A frontend on another domain, or behind a tunnel during development, never gets the cookie, so its preview frame cannot read the draft.
Any user who can edit a consumer can also point its preview target at any host. The editor's preview then loads in a frame from that host, and with a token in its URL, that host can read the draft.
Proposed resolution
- Add a
[preview_token] URL token. With Simple OAuth installed, it is an access token for the editor, issued to the target's consumer, with the scopes the editor would get by signing in to that consumer. Simple OAuth accepts it as a bearer token, so the frontend reads the draft without the cookie. It lasts 15 minutes by default.
- Keep Simple OAuth optional. Without it, or for a consumer without the Authorization Code grant, the token is empty.
- Let a
settings.php target name its consumer by client ID, so it can get a token too.
- Add an allowed target hosts list. The consumer form and the targets API refuse a URL on any other host, and the URL field lists the allowed hosts. A saved target on a host that is no longer allowed leaves the Frontend picker, and does not stop its consumer saving. A URL with a backslash is refused, since PHP and browsers read its host differently.
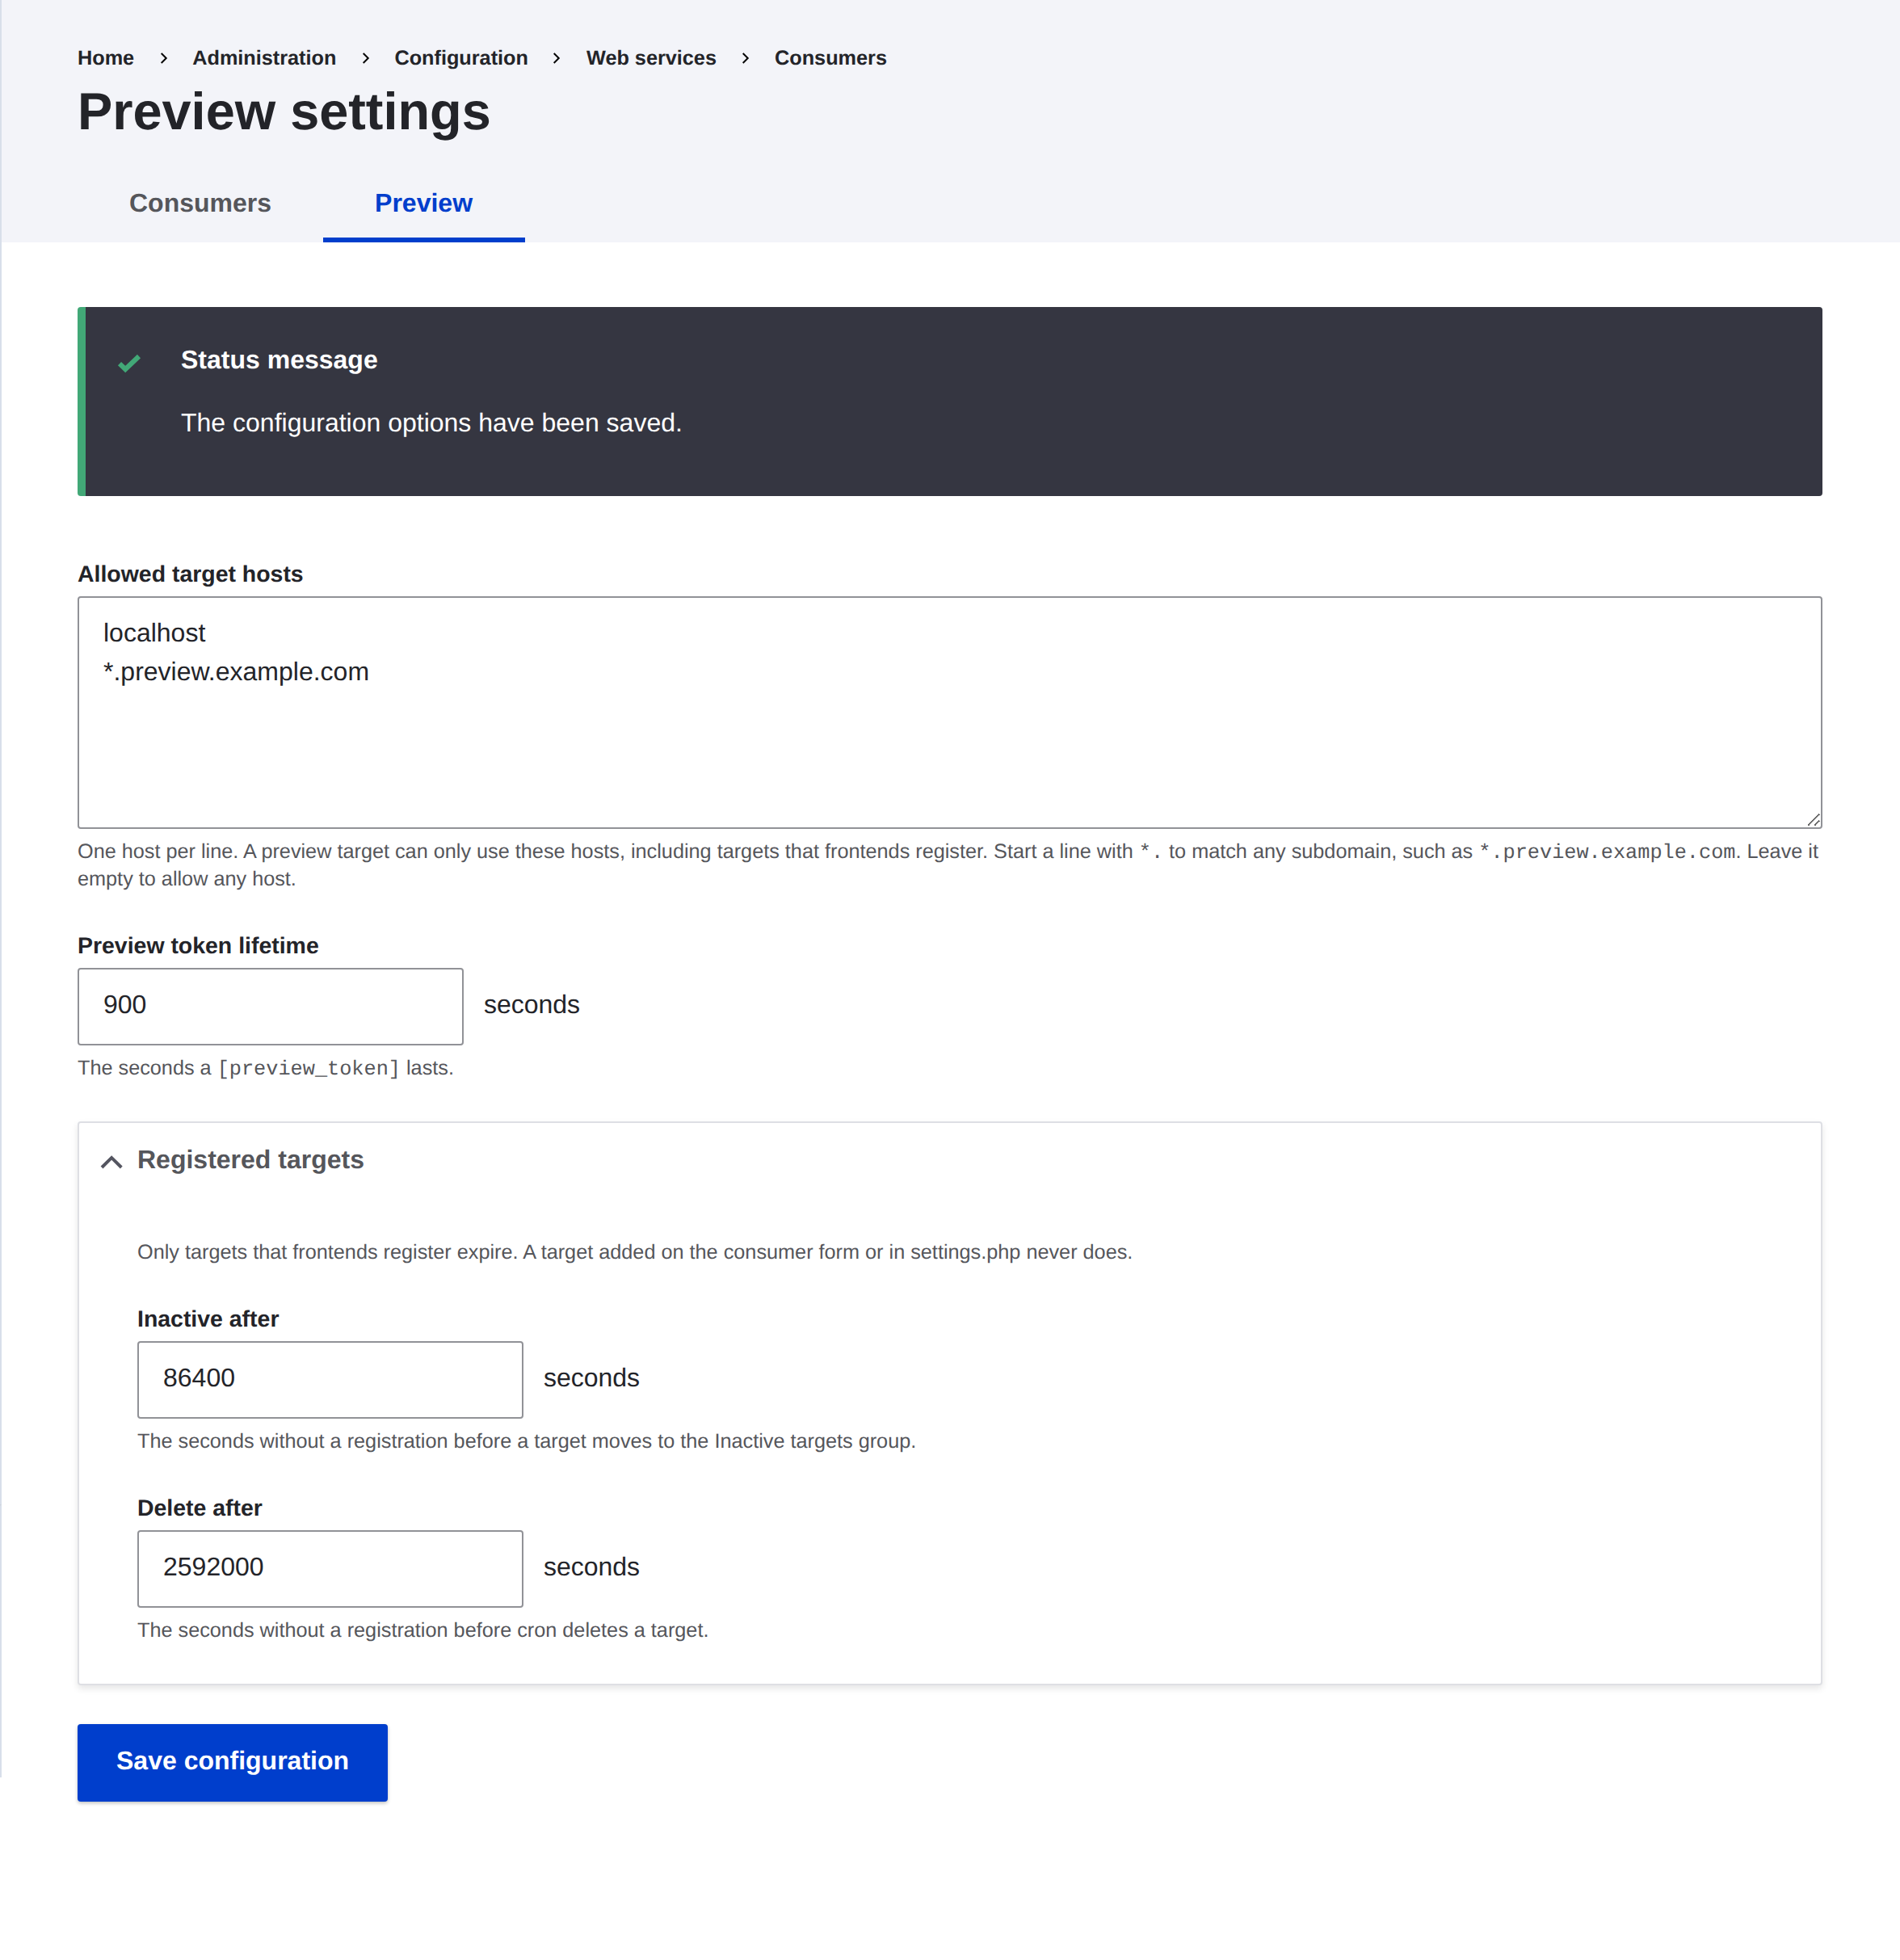
- Add a Preview tab beside Consumers for the allowed hosts, the token lifetime and the target expiry limits. The expiry limits move from
$settings to config.
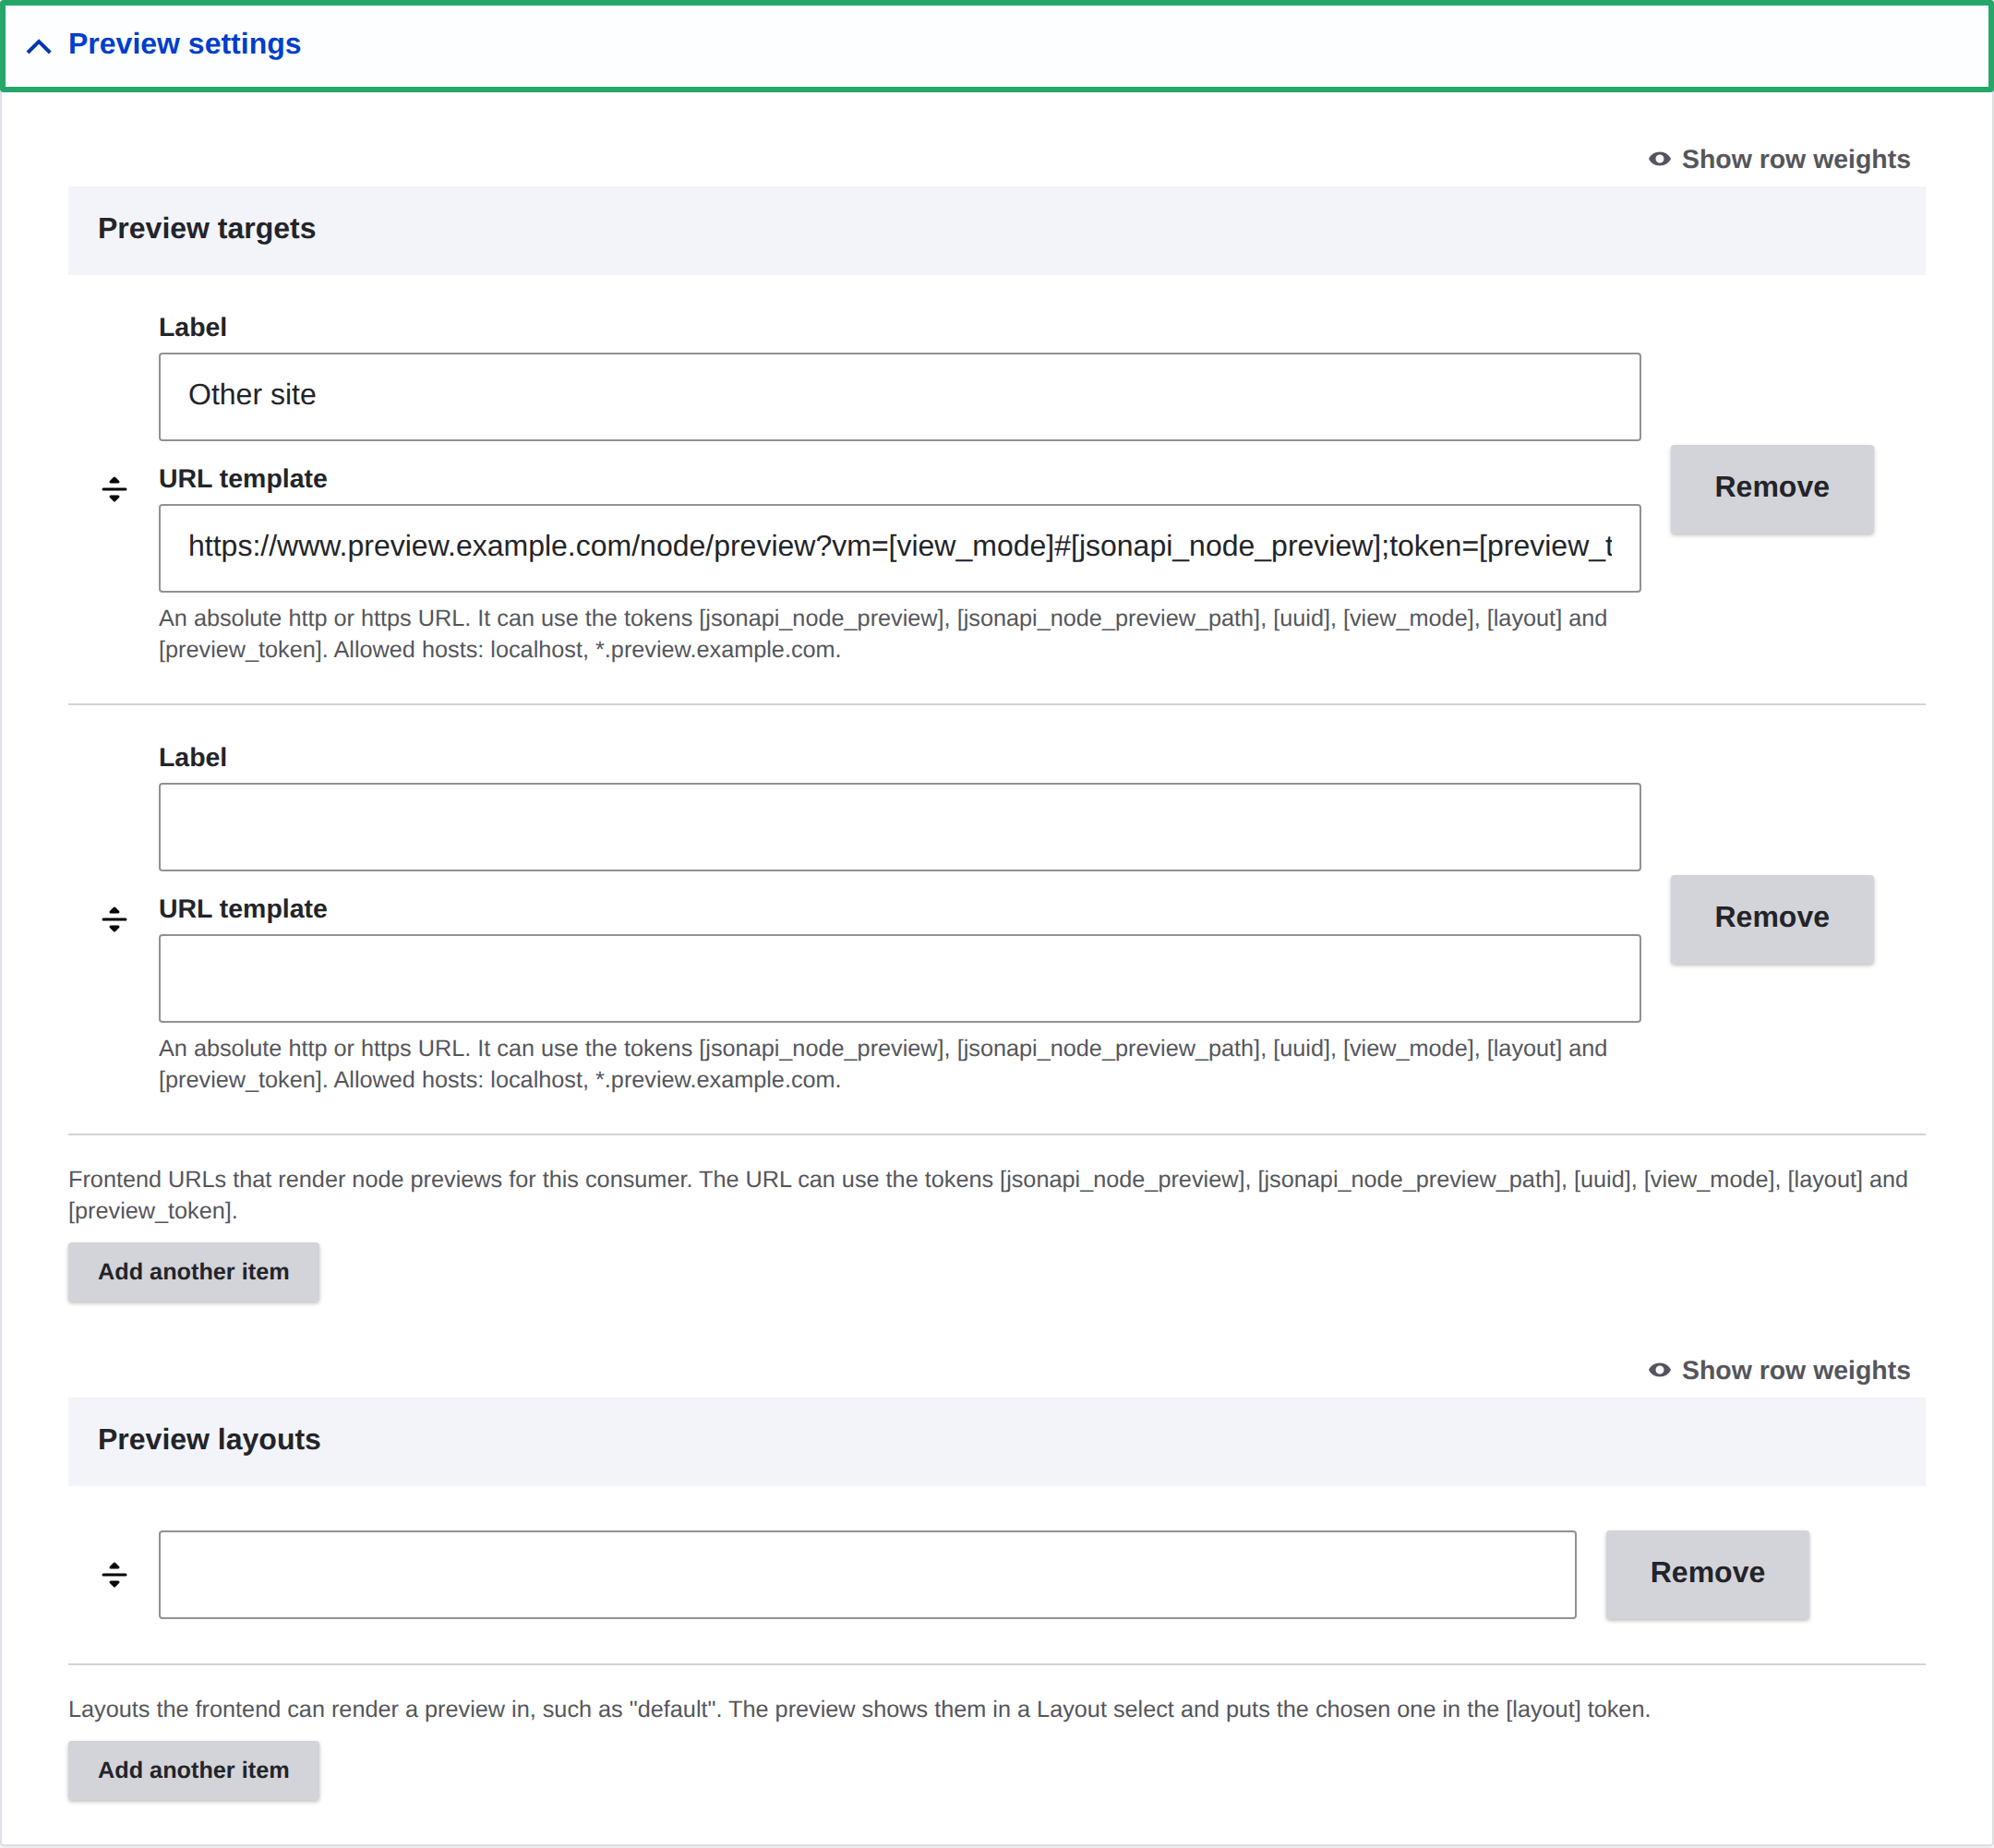
- Put the consumer form's Preview targets and Preview layouts in a closed Preview settings group, which opens when one of its fields has an error.
Remaining tasks
- Review the merge request.
User interface changes
- A Preview tab at
/admin/config/services/consumer/preview: screenshot.
- The Preview settings group on the consumer form, with the allowed hosts under each URL: screenshot.
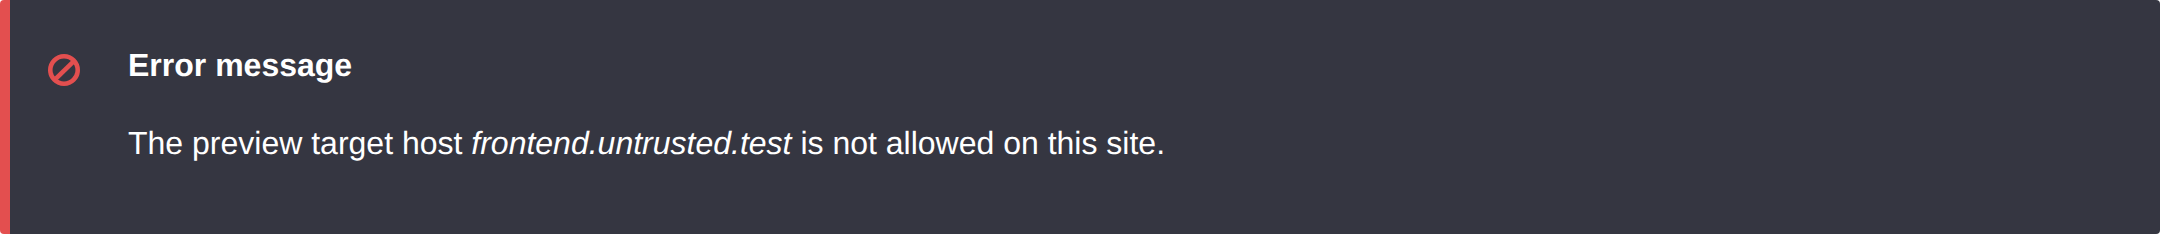
- The error for a host that is not allowed: screenshot.
API changes
- Adds the
[preview_token] URL token and the consumer_node_preview.preview_token service.
- Adds
getAllowedHosts() and isAllowedHost() to PreviewTargetsProviderInterface. resolveUrl() takes an optional consumer.
- The targets from
getAllTargets() gain a consumer value, and a settings.php target takes a consumer key.
- Adds the
consumer_node_preview.settings config, with allowed_target_hosts, token_lifetime, inactive_after and delete_after. A site that set the last two in $settings sets them in $config instead. No release has had them yet.
- Suggests Simple OAuth 6.1 or later.
Data model changes
None.


 Show commands
 changes

Comments
Comment #4
deciphered