Trying to write a custom module tying in ACL with commerce_license (to purchase access to content), but I'm not sure I'm implementing the ACL API correctly. Everything seams to be in the database, however. I'm probably missing a step, but I'm not sure what that is.
User is uid 3. Node I'm trying to access is node/23. ACL is 16.
ACL is listed in acl table. Node is listed in acl_node table, with grant view only. User is listed in acl_user table.
mysql> select * from acl WHERE acl_id = 16;
+--------+----------------------+-----------+--------+
| acl_id | module               | name      | number |
+--------+----------------------+-----------+--------+
|     16 | commerce_license_acl | ACL_4_23  |   NULL |
+--------+----------------------+-----------+--------+


mysql> select * from acl_node WHERE acl_id = 16;
+--------+-----+------------+--------------+--------------+----------+
| acl_id | nid | grant_view | grant_update | grant_delete | priority |
+--------+-----+------------+--------------+--------------+----------+
|     16 |  23 |          1 |            0 |            0 |        0 |
+--------+-----+------------+--------------+--------------+----------+


mysql> select * from acl_user WHERE acl_id = 16;
+--------+-----+
| acl_id | uid |
+--------+-----+
|     16 |   3 |
+--------+-----+
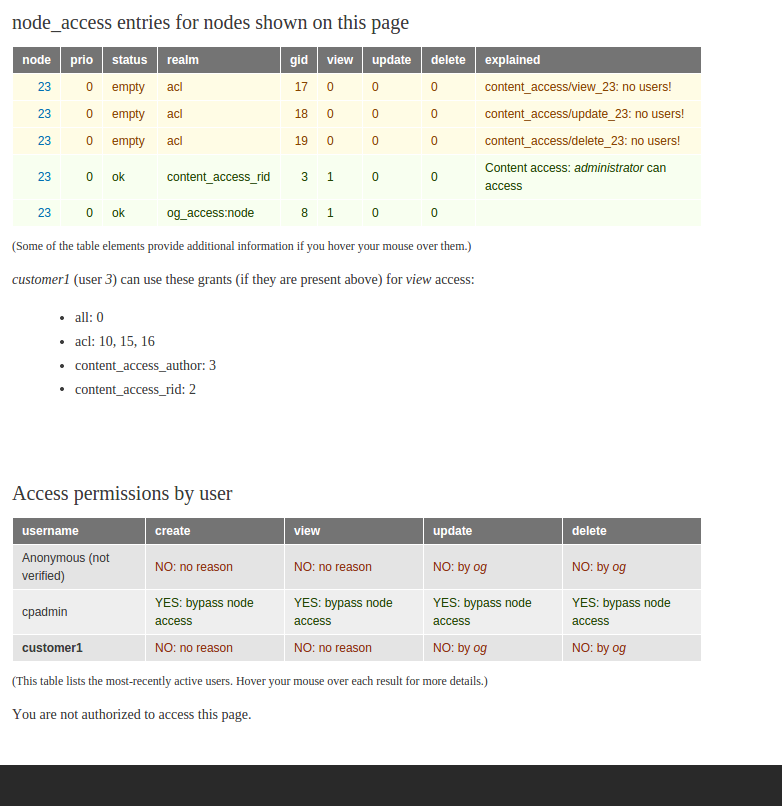
Attached is DNA screenshot showing user is not authorized (logged in user is uid 3).


Comments
Comment #1
salvisYou're missing the entry in the {node_access} table.
Try calling node_access_acquire_grants() on node 23 after setting up ACL.
Comment #2
joshua.albert commentedSorry, I'm not sure what you mean.
You mean I should place this in the save() function of my license plugin (this is where I'm creating the acl and adding the node and user to it)? Doesn't rebuilding the access permissions call node_access_acquire_grants()? I've rebuilt access permissions and I'm still not getting anything.
Here is the code for my plugin:
I run this, test it out, and the same thing - there are records in the acl tables, but nothing in the node_access table.
Comment #3
salvisYes, but you have to call node_access_acquire_grants() (yes, as in #2) because you don't want to rebuild all the access permissions every time.
Did you implement hook_enabled()?
ACL will not return its NA records for your module if your module does not confirm that it's active.
Also, your module should implement hook_disable():
Comment #5
joshua.albert commentedYes, I've implemented both hook_enabled() and hook_disable().
I'm still not getting anything listed in the node_access records.
Comment #6
joshua.albert commentedComment #7
joshua.albert commentedI've noticed in the acl_node_grants() function, we are returning an array of acl ids. I don't see anything in the node_access records with a realm of "acl".
When are the acl tables converted to node_access records, if not in the acl_node_grants() function?
Comment #8
salvisThat's the query side of node access.
In https://api.drupal.org/api/drupal/modules!node!node.module/function/node...
After your module has set up the ACL records, it must call that function. This will call acl_node_access_records() which will return the data that goes into the node_access table.
But I thought you were already calling node_access_acquire_grants()...
Your DNA screenshot...
... does show 'acl' records, but it says "no users" for node/23. So it seems like acl_add_user() is not getting called as you expect. This may well cause acl_node_access_records() to not return them, because they'd be irrelevant — I'm not sure.
If you hover your mouse over "empty" it'll tell you what exactly it means.
Comment #9
joshua.albert commentedSorry. That was a month ago. There have been some modifications to the code recently, but I didn't think they would affect anything. However, something must have broke somewhere along the way, because now the acl realm isn't showing anywhere in the node_access table or DNA, even though the acl, acl_node, and acl_user tables are populated correctly.
My other module (which implements hook_node_access, hook_node_access_records and hook_node_grants) seams to be working fine, as well, here:
Comment #10
joshua.albert commented"it says "no users" for node/23. So it seems like acl_add_user() is not getting called as you expect."
Here are my acl tables:
If the acl_add_user() is not being called, how is the user being added to the acl_user table?
Comment #11
salvisWell, that's the conclusion I drew from what the original DNA showed. What is it showing now?
After you've made the screenshot, have you tried to rebuild permissions? Does that make any difference?
Your ACL tables look ok.
Comment #12
joshua.albert commentedThe DNA listing is showing that everybody, including anon users, has access to node 23.
Hovering over "default" shows the message "Default grant supplied by core in the absence of any other non-empty grants; in {node_access}."
As shown above, this is what I have in the node_access table:
To answer your question, yes, I've cleared cached and rebuilt permissions.
Comment #13
joshua.albert commentedFigured it out. It was the enabled() hook. I had misspelled the function name, so acl_node_access_records() was bypassing and not returning the grants. Oops. Thanks for your help.
Comment #14
salvisOk, thanks for following up.