I did not submit this to the Security Team because they are already aware and it was made public in 2016: https://www.drupal.org/forum/newsletters/security-public-service-announc...
The purpose of this issue is to fix the exposure, at least for Webform, with a very simple patch.
Problem
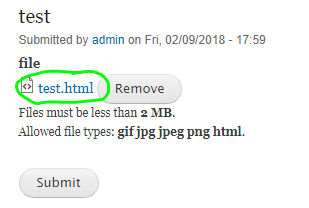
The full web-accessible path of any uploaded file is reported to the (possibly anonymous) visitor who uploaded the file, even if that visitor does not have submission result access. This file is uploaded and web-accessible without any other form validation being enforced (including CAPTCHA), and (if the submission is never completed) will stay on disk at the given location until the next cron run after 6 hours.
There is no simple means of locking down these file uploads, without requiring users to create logins. Using a private file system will not prevent access or misuse of files - they're still potentially accessible by 3rd parties. The obvious mitigation step of using randomly generated subdirectories (as Google Docs, OneDrive, etc. use) does nothing, because the complete path is still returned to the user.
With the path, malicious users can (not an exhaustive list):
- Use the site for free 6-hour webhosting (which can mean a lot with the speed of bots)
- Potentially craft same-origin XSS (normal browser security will be ineffective)
- Enumerate files uploaded by other users
- Send legitimate-looking phishing emails (unsuspecting users will see document links coming from their own server)
- SEO spam (as mentioned in the PSA) - files are uploaded and then submitted to search engines to borrow (and hurt) the reputation of the victim site
Reproduction
You can reproduce this by:
- Enabling the module
- Creating a Webform with a File component
- Optionally, create mandatory fields or validation rules, enable CAPTCHA, etc. - it will have no impact
- As a user with access to submit to the Webform (often anonymous), upload a file by clicking the "Upload" AJAX button instead of submitting the form, or intentionally fail validation of some other field (don't enter a required field, or purposely don't pass CAPTCHA).
- Observe that the form (either when updated via AJAX or after reloading with form errors) will have a link to the uploaded file next to the "Remove" button.
But why?
I can think of no reason that the file's ultimate address is necessary to display to the user that just uploaded the file. They don't need to be able to click it and retrieve a copy - they just uploaded it. There are a myriad abuses possible with this information, and very few legitimate reasons to display it, so why not remove it?
Solution
The underlying problem with the File module can't be fixed, but there's no reason that Webform should provide another instance of the same problem. webform/components/file.inc already implements as webform_file_allow_access() function. Simply overwrite the output in that function to strip the file link, preventing unnecessary information disclosure. Patch provided.



Comments
Comment #3
jay.dansand commentedResubmitting with corrected paths so hopefully testbot will be happy.
Comment #4
jay.dansand commentedARGH. Embarrassing regex failure. Realized just as I clicked "Save." Wish there was a 30-second "Undo" button.
Comment #6
David_Rothstein commentedI am not sure this would be too useful without also implementing the other step mentioned in the issue summary:
On most Drupal sites, the file directory is easily guessable, so this patch on its own wouldn't bring much benefit, would it? The main thing it would do is make it harder for legitimate users to check/preview the file they just uploaded (e.g. to double-check that it uploaded correctly).
But combined with randomly-generated subdirectories, I suppose it could be useful. Would probably make more sense as an optional feature in core (with Webform just inheriting the use of that option) though, so that any file field, Webform-related or not, could use it?
For now, though, the best solution is to do what is recommended in https://www.drupal.org/forum/newsletters/security-public-service-announc... - if you don't want untrusted users uploading publicly-visible files to your site, configure the file fields to use the private file system, and configure the access controls so that those private files won't be visible to people who aren't supposed to see them.
Comment #7
liam morlandWebform is following the existing behavior of Drupal core. If it is going to be changed, it needs to be changed in core.