

Closed (fixed)
Project:
Cave your trolls
Version:
6.x-1.0-beta2
Component:
Code
Priority:
Normal
Category:
Feature request
Assigned:
Unassigned
Reporter:
Created:
18 Aug 2009 at 17:02 UTC
Updated:
2 Jan 2014 at 19:06 UTC
Jump to comment: Most recent, Most recent file

Comments
Comment #1
danielb commentedI believe troll can do what you're after regarding IP addresses. There is no alternative at the moment than using troll for ip banning. I understand there are some drawbacks to the troll module method, but it was the quickest way for me to give IP support to this module. I would eventually like to make an IP list module that can service this one, like troll, but more appropriate for use with a module like this.
Comment #2
danielb commentedComment #3
kaakuu commentedFixed ?
I am unable to do this simple operation -
username : Robert. [] Enable cave for him
Neither Troll + Cave helps, nor any documentation to guide.
Things are not intuitive, and I do not how many hours have to be given to get the settings right and things work for me. I am willing though to learn and spend the time once I avail the time.
May be I can after that and reopen it if needed with greater details.
Thanks.
Comment #4
danielb commentedAlright I'm gonna look into making this more usable.
Comment #5
danielb commentedHere are some instructions for using it with Troll.
- Go to the admin/user/troll
- Search for the user you want, and get their IP addresses
- Add their IP to the list at admin/user/troll/ip_blacklist/import
- go to admin/user/troll/ip_blacklist/punishment
- Tick the Cave option.
Comment #6
kaakuu commentedOK, Thanks a lot, that should be helpful.
The MAIN problem with IP is that most users in our scenario or in many countries have dynamic IPs. Those doing net from cybercafe or institutes also have changing IPs. So "cave" via IP route becomes pretty unusable apart from the fact that there are so many steps one has to do. We need to "cave" an user directly by user name.
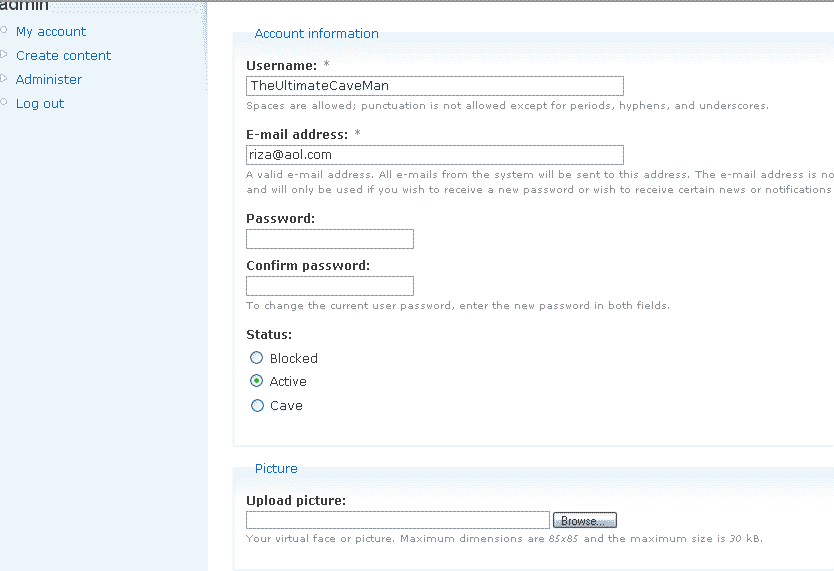
Each user has an easy [Active] [Block] option - making this [Active] [Block] [Cave] would make the things actually work as intended apart from the fact that things will become a simple administrative task.
Comment #7
kaakuu commentedDiagram to explain above.
Comment #8
danielb commentedI would like to make a module that allows you to maintain several categorised list of user Ids or user IPs, easily see the user's different IP addresses, as well as seeing which users use the same IP address, suggesting possible IP ranges and masks to identify the user with, finding the user's unique IP addresses, and blocking future unique IPs they may try to log in with. Then you could add user control features to each category of list, such as banning, or the effects of the cave module.
Comment #9
kaakuu commentedThanks. That sounds great and I hope that will be of great use.
In addition a simple operation like [block user] [enable cave] http://drupal.org/files/issues/cave.gif
would be a welcome urgent addition to this module as IPs horribly change as user changes ISP, has dynamic IPs and may even use various proxy services.
Comment #10
danielb commentedI have added the ability to activate a checkbox in the user's account page to cave them. The obvious flaw is they can log out and see that their posts are removed. This is why we need the ability to match IPs with users, and perhaps even tag their browser with a cookie, so we can attempt to identify them when they log out.
Also with some testing I have found that while nodes and comments are removed from listing, the node will still show if you go to the node page, and the comment count is wrong. This was probably true of the 'troll' method as well, I just didn't notice?
Comment #11
kaakuu commentedThanks.
The same applies to IP. Many ISPs have now wide dynamic range and using another IP or proxy service the user can very well find out that their posts have been removed :)
YAY!! Is that now available in the stable downloadable version?
Comment #12
danielb commentedYeah but it's not really a simple matter of accidentally seeing it when they're logging out. They would have to suspect they are being caved to evade detection - and for many users it is impossible to do this. The dynamic range is a bit annoying - I wonder if there is a way to detect a range of IPs and make suggestion to the admin whether to assume anything on that range belongs to that user - and at least to see what other users it might affect.
Do not assume this module is stable - please test it on your site!
Comment #13
kaakuu commentedNo, not a matter of accidental! Users from most ISPs or cybercafes or institutes can have such variety of ISPs and IPs so that they by 'chance' or by will can easily see so. We also have users who have mobile browsing while on the go and at home regular broadband. This is getting common. Anyway thanks.
Edited - To remove a question I asked.
Comment #14
danielb commentedIt is obvious you don't actually read anything I write, so I'm not going to respond any further.
Comment #15
kaakuu commentedSorry if anything sounded like that. I may have failed in communicating to you.
I am trying my best to use this module and make it popular as far as I can.
I have spend hours testing and trying it. And will do so more asap.
It will be nice to know what made it obvious that I do not read what you write.
Anyway, I appreciate the help I got from you and am really grateful that you created this module which actually needs to be part and parcel of Drupal.
Thanks a lot.