

Closed (duplicate)
Project:
Drupal core
Version:
8.0.x-dev
Component:
user.module
Priority:
Major
Category:
Task
Assigned:
Unassigned
Issue tags:
Reporter:
Created:
28 Aug 2015 at 18:39 UTC
Updated:
27 Sep 2015 at 16:02 UTC
Jump to comment: Most recent, Most recent file


Comments
Comment #2
borisson_Comment #3
joelpittetThanks @borisson_ feel free to grab as many as you'd like we are just laying out the plan, you are quick on the trigger:)
Are you on IRC?
Comment #5
borisson_@joelpittet, not on irc or online at all in the next week.
Comment #6
joelpittetDang cross-pollination! this failed on migrate D6. I'll see how that one fairs on it's own, this may need postponing or merging with that one.
Comment #7
andypostTokens should be replaced properly, this fixes migrations
Comment #8
joelpittetGood catch @andypost thank you, this one is good to review without any migrate integration.
Comment #9
joelpittetPointing out the locations for manual testing. Also there is a double escaping bug here from Html::escape() into @ placeholder
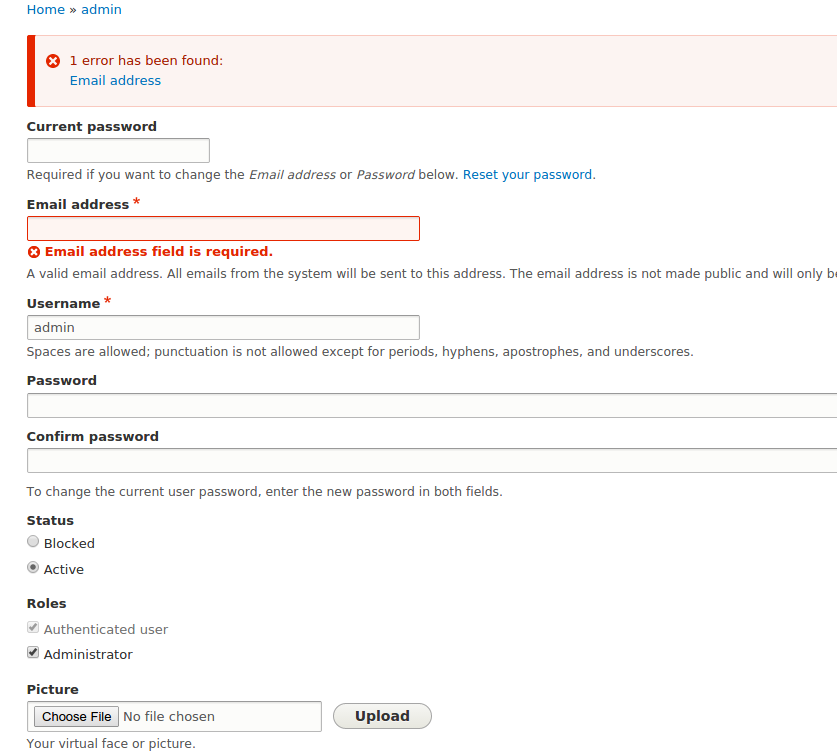
This is on the user account page.
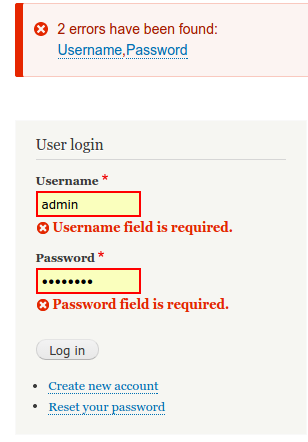
Validation names
We don't need the Html::escape() here and that will likely lead to double escaping.
This is a number so no need to test.
These can be found on the help page and should be straight forward.
Comment #10
hog commentedEdited patch #9
Comment #11
hog commentedComment #12
hog commentedComment #14
joelpittet@HOG last patch had 0 bytes. Could you comment of a slight indication of what you are doing for each patch?
Not sure what you are attempting in #10 or #12
#9.3 to be clear is just removing the pre-escaping done by
Html::escape()Everything else is notes on where to find things for manual testing
Comment #15
hog commentedRevert #9 3 comment.
https://www.drupal.org/files/issues/interdiff-2559459-7-12.txt
Comment #16
hog commented#7 patch not applying, i'm rerolled it.
Comment #17
hog commentedComment #18
andypostLooks enough
Comment #19
catchPostponed on #2558791: "!"-prefixed tokens should Xss::filterAdmin() but not affect safeness.
Comment #20
justachris commentedClosing this, splitting by module was not the ideal approach to removing !placeholder. Marking as duplicate of #2506427: [meta] !placeholder causes strings to be escaped and makes the sanitization API harder to understand, since the chosen approach is / will be outlined there, please refer to it for any additional action.
Comment #21
sutharsan commentedPatch now merged into #2506445-140: Replace !placeholder with @placeholder in t() and format_string() for non-URLs in tests.
Comment #22
xjm