We were trying to test out Iframe integration payment method, but for some reason it did not work. Every time we got re-directed back to payment review page.
Checking the logs on SagePay shows us this message - Transaction completed but Vendor systems returned INVALID or ERROR in response to notification POST. Transaction CANCELLED by the Vendor..
After few unsuccessful attempts I added a line in "commerce_sagepay_server.inc" to push out on watchdog log what's happening there. My code looks like this
watchdog('test_error', 'Order message %message for order %order_id', array('%message' => $notification['message'], '%order_id' => $order_id), WATCHDOG_NOTICE);
I put it around line 422.
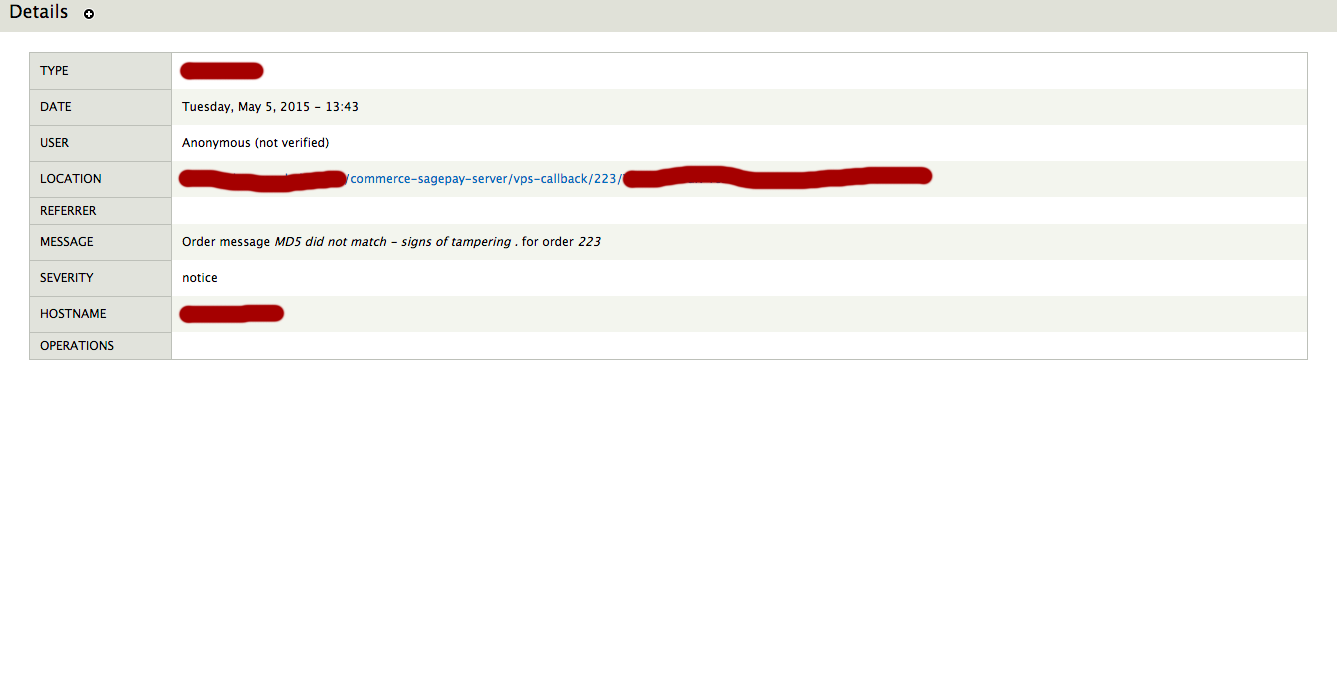
Finally with this small hack I managed to get the contents of $notification['message'], which were - "MD5 did not match - signs of tampering" (see screenshot attached).
Contacted SagePay, they responded that this is our side to make sure that both $_REQUEST["VPSSignature"] and concatenated md5 hash of message contents should match.
Is there any idea why these two do not match?
FYI - We were using SagePay test server.


Comments
Comment #1
pasive commentedManaged to solve the problem.
It turns out to be a configuration problem. As SagePay Documentation states - http://www.sagepay.co.uk/file/15366/download-document/SERVER_Integration... on page 68
So we just went to SagePay settings admin page on Drupal and changed Capital case to lower case. Was easy though.
Later I realised that for some reason SagePay themselves may send you vendor information in Capital case.
So, case of a human error is quite obvious in this situation.
This patch ensures that Vendor name is always lover case before hashing.
Comment #2
pasive commentedComment #3
m1n0 commentedThanks for this patch, definitely makes sense, I propose a small change here, make sure that vendor_name is always lowercase, even if the override is on - just for the sake of cleaner and more readable code.
Comment #5
ikos commentedCommitted thanks!