Many people have reported great success when using this module to prevent spam bots and other forms of spam. Some of these people's stories are collected below, for those who wish to know:
I installed Honeypot yesterday and within a few minutes it was blocking 100% of my spam! It's like watching a zombie trying to walk through a wall, over and over again. :-)
If you have control over your webserver and can install Fail2ban on the server, you can add configuration that will automatically ban bots on the system level if they trigger enough Honeypot rejections, saving your webserver from having to deal with these bots in the first place!
Since Drupal (and, by extension, Honeypot) writes to the system log, we can use fail2ban to ban IP addresses of hosts (bots) that have too many failed login attempts.
Honeypot form protection means that an invisible field is added to a form. If this invisible field is filled out (bots will usually put in a value), then the form will return an error. Normal users (read: human beings) won't ever see the field, so they won't fill it out. Even if they do, the field is labeled in such a way as to indicate the human shouldn't fill out the field.
Honeypot uses both the honeypot and timestamp methods of deterring spam bots from completing forms on your Drupal site. These methods are effective against many spam bots, and are not as intrusive as CAPTCHAs or other methods which punish the user [YouTube].
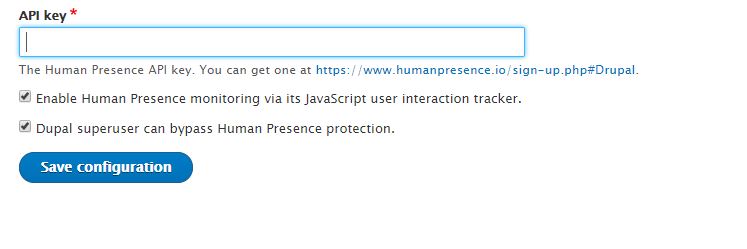
Visit admin » config » development » human-presencefor settings
Populate API credentials, either entering API key or you can request API key using your company and username
It is best practice to store API credentials outside of the database and your source code repository. Consider setting the credential variable hp_api_key as a server environment variable and bringing it into your Drupal configuration via the $conf array in your settings.php file instead.